There is a moment, in every online account that touches real money, when everything is still reversible. It is the moment before the first deposit. Up to that point you have spent nothing but time; past it, you are relying on other people’s processes to get your money back. Most of the painful stories this site documents — frozen balances, vanished agents, payouts that never came — trace back to checks that were skipped in that moment, because the person was in a hurry and the deposit screen was not.
What follows is the routine worth running every single time, whatever the platform, whatever the app, whoever recommended it. None of it requires technical skill. All of it requires the willingness to wait one more day before paying.
Start with the counterparty, not the product
The first question is not “is this platform good” but “who exactly receives my money, and what do I know about them?” Those are different questions because, in a large part of this market, the entity you pay is not the platform at all. It is an intermediary — a person or small operation issuing access to platforms they do not run. Sometimes that arrangement works smoothly for years. Sometimes the intermediary stops answering on the day a withdrawal is due. The difference is rarely visible from a WhatsApp chat window.
So before anything else, name the counterparty. If it is a company, it has a website older than a few weeks, a support channel that is not one phone number, and a presence you can find from more than one direction. If it is an individual with a payment handle and a persuasive manner, you already know everything you need to know: you would be making an unsecured personal loan to a stranger, dressed up as a deposit.
Understand the model before you fund it
A surprising number of people fund account types they cannot describe. If the arrangement involves issued credentials — an account someone opens for you rather than one you open yourself — read up on how that model works before any money moves, because its failure modes are specific: the issuer controls recovery, the issuer sees the balance, and the issuer stands between you and every payout. The cricket id guides cover the mechanics of that issued-account model in detail, and fifteen minutes there is worth more than any reassurance a seller types into a chat.
The test to apply afterwards is simple: can you now explain, in two sentences, how money gets out of this arrangement and who has to cooperate for that to happen? If the answer involves more than one party whose name you do not know, the model has told you its risk already.
Run the name line
Take three names and put them side by side: the name on your identity document, the name on the account or profile being created, and the name on the bank account or wallet the money will eventually return to. They must match — exactly, not approximately. This single check prevents the most common payout failure that exists, because verification systems compare these strings at withdrawal time, long after the deposit sailed through without question.
While you are at it, run the same line on the other side. Whose name is on the account you are paying into? A business takes payment into a business identity. A “verification desk” that wants its fee sent to a personal UPI handle belonging to a third name you have never seen is not a verification desk.
Test the exit before you trust the entrance
Everything about a first deposit is designed to be smooth, so a smooth deposit tells you nothing. The informative experiment is the reverse trip. Where the arrangement allows it, the sequence worth running is deliberately dull:
Deposit the smallest amount the system accepts.
Use the account normally for a short period — enough for the balance to be real rather than promotional.
Request a withdrawal of a similarly small amount.
Time it, document it, and watch what is asked of you along the way.
A clean small withdrawal does not prove the arrangement is safe forever. But a small withdrawal that stalls, sprouts fees, or triggers demands for further deposits has just saved you from discovering the same behaviour with a month’s salary in the balance. The stories collected in the piece on deposits that never arrived almost all share one feature: the first real test of the exit happened with a large amount, because the small test was never run.
Refuse the pre-payment vocabulary
Certain words, appearing before or during a first deposit, end the conversation on their own. Activation fee. Unlock charge. Verification deposit. Refundable security amount. Processing fee to release the bonus. Legitimate arrangements take their cut from play over time; they do not invoice you for the privilege of giving them money. Any fee whose stated purpose is to make your own funds accessible is not a fee — it is the product, and you are the sale.
The same applies to urgency. Countdown timers on “special deposit rates”, agents who need the transfer today, offers that expire while you are still asking questions — pressure is information. Processes that are safe at speed are also safe slowly, so anyone insisting on speed is telling you which kind of process this is.
Protect the recovery spine
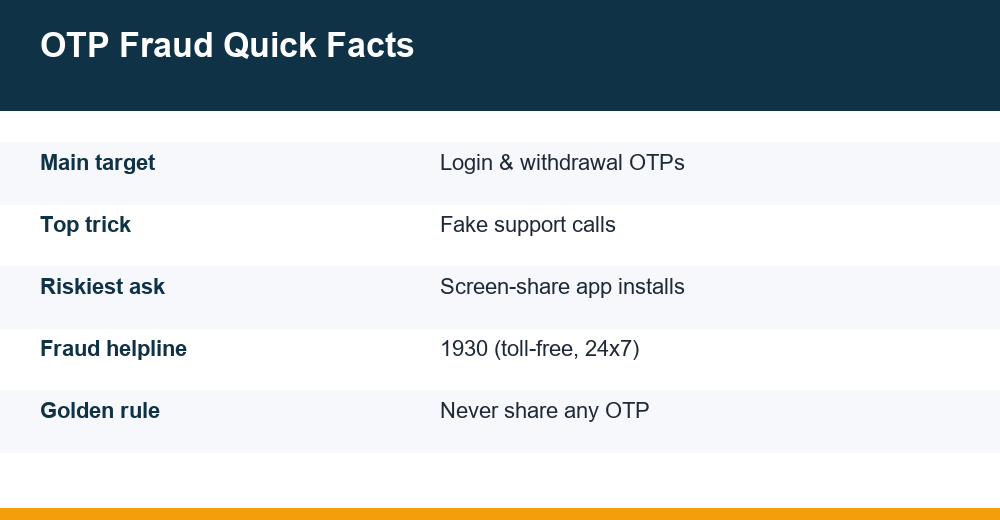
Before funding anything, look at what the account hangs from: a phone number and an email address. Both should be yours alone, current, and secured — because whoever controls them controls the account, its balance and its recovery. That means the OTPs arriving on that number are as valuable as the money itself, a point covered at length in the guide to protecting codes and one-time passwords. No counterparty ever needs an OTP read out to them; the request itself is the diagnosis.
A shared family phone, a recycled SIM, an email with a password used in six other places — each is a quiet structural weakness that costs nothing today and everything on the wrong day.
Start the file
The last check is not a check but a habit: open a folder — on the phone is fine — before the first rupee moves. Into it goes the counterparty’s details as they presented them, the payment confirmation, the account credentials’ recovery details, and every screenshot that later feels even slightly important. Dates matter; capture them.
The folder will probably never be needed. That is the point of it. Formal complaints, bank disputes and fraud reports all run on documents and reference numbers, and the people who resolve such things fastest are invariably the ones who can produce a tidy, dated trail rather than a memory of a chat that has since been deleted. The habit costs two minutes per event. Its absence has cost people everything they put in.
The routine, condensed
Name the counterparty. Understand the model. Match the three names. Test the exit small. Refuse pre-payment fees and manufactured urgency. Secure the number and the inbox. Keep the file. Seven checks, none requiring expertise, all requiring only the one thing a deposit screen is engineered to take away — patience.
Nothing in this routine makes real-money play profitable; the arithmetic of the games is untouched by paperwork, and the expected direction of money over time is away from the player. What the routine changes is the failure mode. People who run it still lose what the games are designed to take. They very rarely lose it to the counterfeit platforms, vanishing agents and unlock-fee artists this site exists to document.
18+. Real-money play carries financial risk. If it has stopped feeling like a choice, free and confidential support is available, and reporting fraud at the national cybercrime portal or on 1930 helps the next person too.
Seeing a withdrawal blocked message is where the panic usually starts, because the screen says almost nothing while the balance sits out of reach. This page sets out what the different kinds of holds actually mean, how the deposit-to-unlock pressure sequence unfolds, and what to do instead of chasing the money. One plain note first: these games are chance-based with a built-in house edge, real money is at risk, and they are for adults 18 and over only.
Table of Contents
Withdrawal Blocked: What It Actually Means
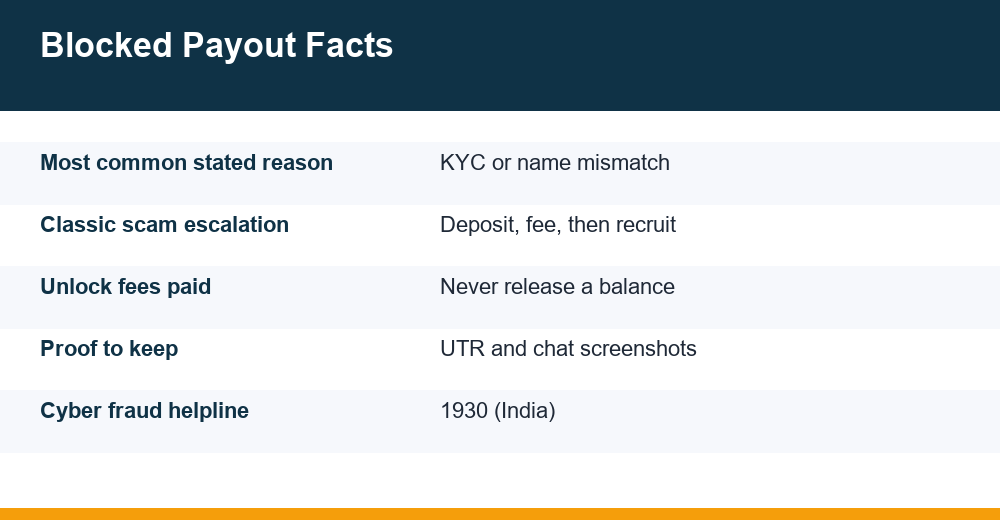
The wording on screen is always short – blocked, on hold, under review – and the explanation is almost always missing. In practice a withdrawal blocked status covers at least four very different situations, and the right response depends entirely on which one you are in: a routine document check, a bonus condition you did not notice, a bank detail that does not match, or a platform that has quietly stopped paying anyone at all.
Telling them apart starts with knowing that a payout is not one action. Money moves through several hand-offs, and a hold can sit at any of them. Only the last stage involves a bank; everything before it is controlled entirely by the platform, which is also why the platform stages are the ones described least clearly.
Wallet balance: funds inside the app, held by the platform until paid out
Withdrawable balance: the portion free of bonus or turnover locks
Payout instruction: the transfer order the platform sends to a bank or UPI channel
Settlement: the bank-side step that actually credits your account
If you are unsure what the normal sequence looks like, our breakdown of colour prediction withdrawals walks through the ordinary request-to-credit pipeline. Compare what you are seeing against that baseline. A delay that fits the published window is operations; a hold with shifting explanations and new payment demands is something else.
Keep one structural fact in view throughout. Every round is independent chance with a margin built into the payouts, so the balance on screen is not savings being withheld from you – it is an amount an operator has recorded in its own ledger. That distinction matters when you decide how much more time, and money, to spend pursuing it.
Why Is a Payout Pending for Days?
Pending is the most common status and the least informative. A small set of causes explains the large majority of stuck requests, and they are worth working through in order of likelihood before assuming the worst.
Incomplete verification: documents not submitted, or submitted and not yet approved
Name mismatch: the bank or UPI account name differs from the registered profile name
Unmet bonus turnover: promotional credit locked the balance until wagering conditions cleared
First payout review: many apps inspect a user’s first withdrawal manually
Amount outside limits: below the stated minimum or above a daily cap
Duplicate requests: cancelling and re-raising repeatedly resets the queue position
Batch timing: some payment desks release payouts only at fixed hours
Most of that list is administrative rather than sinister, and a hold that clears inside the stated window is normal. What matters is the pattern over several days. If support gives you a specific, checkable reason and the request moves once you fix it, the system is working. If each reply gives a new reason and nothing ever moves, you are not in a queue.
There is also a timing detail worth noting. Holds appear far more often after an unusually large deposit or an unusually large win than during ordinary small play. That skew is one of the clearest early signals in complaint threads, and it is the point at which to slow down rather than deposit again.
Why an App Asks for Another Deposit to Unlock a Payout
Because it works. A user with a frozen balance is already emotionally invested, and a small extra deposit feels cheap next to the amount apparently waiting. The demand is usually dressed up in operational language: a wallet activation, a tier upgrade, a minimum turnover top-up, a “matching” deposit to confirm the account is genuine.
None of those are real payment mechanics. A payout instruction does not need an incoming deposit to execute, and no bank or UPI channel requires the recipient to send money before receiving money. When a platform ties your existing balance to a new payment from you, the balance has become the hook rather than the obligation.
The sequence in reported cases is remarkably consistent, which is what makes it recognisable. A first hold with a plausible reason. A modest deposit to clear it. A larger demand framed as a fee. Then, often, an invitation to recruit friends or move to a “VIP” channel where the payout supposedly happens faster. Each step raises the sunk cost and the reluctance to walk away.
Deposit requested specifically to release an existing balance
Thresholds that move upward each time you reach them
Support shifting from in-app chat to WhatsApp or Telegram
A named “manager” or “agent” handling your case personally
Payment requested to a personal UPI ID or individual account
Promises of priority processing in exchange for recruiting others
One related confusion is worth separating out: a deposit that genuinely never arrived is a different problem with a different fix, and we cover it in our notes on a deposit not credited. Mixing the two up is common, and it gives a stalling operator room to blame the bank for something that never left its own ledger.
Should You Pay a Fee or Tax to Release Winnings?
No. Not a processing charge, not a verification fee, not a clearance payment, not a “tax deposit” to be refunded later. A payment demanded as the condition for releasing your own balance is, in every reported pattern, the second half of the same scam rather than a step toward a payout. Paying it almost never produces money; it produces a new demand.
The framing is deliberately bureaucratic because bureaucracy sounds unavoidable. It also exploits a real asymmetry: ordinary financial life does involve charges and deductions, so an invented one does not feel absurd. The test is simpler than the vocabulary suggests – a legitimate deduction is taken from the amount being paid, never collected from you in advance through a separate channel.
What you are told
How it is framed
What it actually is
Pay a processing fee
Bank charges for large transfers
Money collected outside the payout
Deposit to activate wallet
Account confirmation step
A new deposit, not a release
Tax clearance payment
Deduction to be refunded later
An advance payment with no refund
Upgrade to a higher tier
Faster payout queue
Escalating demand on the same balance
Recruit users to qualify
Loyalty or referral condition
Pressure to involve other people
The entries above describe how these demands are typically worded in complaints, not an official schedule of anything. Treat the middle column as sales language and the right-hand column as the function it serves. Once a release payment enters the conversation, the useful question stops being how to get the balance out and becomes how to stop the loss where it stands.
Recruiting deserves its own line. Being asked to bring in friends or family to qualify for a payout turns a personal loss into other people’s losses, and it is the point at which walking away protects more than your own money.
Six Steps When a Withdrawal Blocked Status Will Not Clear
When the obvious administrative fixes are done and nothing has moved, work through a fixed sequence rather than improvising. The order matters: it preserves evidence before anyone has a reason to delete it, and it stops the escalation before it costs more.
Stop depositing. Freeze your own outflow before doing anything else, whatever the app is promising.
Capture the current state. Screenshot the request, the status, the balance and the transaction history today.
Ask support, in writing, for one specific thing: the exact reason and the exact step needed. Keep the reply.
Fix only genuine details once – a name spelling, an account number, a UPI ID – and resubmit a single request.
Check your own bank statement to see whether any credit, reversal or partial payment actually arrived.
If nothing moves and new payments are demanded, switch from recovery mode to reporting mode.
Step six is the one people resist, because it feels like giving up on the balance. In practice it is the step with the best odds attached: reporting early, while any funds may still be traceable, does more than weeks of chat messages. Chasing a withdrawal blocked notice through the same support channel that created it rarely changes the outcome.
Resist the urge to open a second account, use a relative’s bank details, or try a different device. All three are treated as red flags by payment teams, and they give a platform a defensible reason to keep the hold in place.
What Evidence to Collect and Preserve
Complaints fail far more often for lack of documentation than for lack of merit. Whoever reviews your case – a bank, a payment app, a police cyber cell – needs to see exactly what happened, in what order, and with which account. Ten minutes of collection beats ten angry messages.
The withdrawal request itself: amount, date, time and the status shown
The full transaction history page, not a single entry
Any UTR or reference number displayed for a claimed transfer
Every support conversation, including agent names, numbers and promises made
Screenshots of any fee, deposit or unlock demand, with the payment details given
The app version, the exact website address, and the account or UPI ID used
Your own bank statement entries covering deposits and any reversals
Export rather than rely on the app. Accounts get closed, chats get cleared and apps get pulled from stores, and anything held only inside the platform can disappear without notice. Save screenshots to your own device or cloud storage, and note the date on each one.
Record the names and numbers used by anyone who contacted you outside the app. Those details are frequently the most useful part of a report, because the same personal accounts and handles turn up across many unrelated complaints.
Who to Complain To When an App Will Not Pay Out
Route the complaint by where the failure actually sits, because sending it to the wrong place costs days. There are three broadly different situations and they go to three different places.
The payment leg failed: your money left but did not arrive, or a transfer bounced – start with your payment app and bank
The platform claims it paid: ask for the UTR and have your bank trace that reference
The platform refuses to pay, or demands a release payment: treat it as suspected payment fraud and report it
For a UPI transaction that genuinely failed or was not credited, the first-line route runs through your own UPI app and bank, with a defined escalation path behind it. NPCI publishes how that works in its UPI dispute redressal mechanism, and it is worth reading before you contact anyone, so you arrive with the right reference numbers in hand.
Where money was taken through a release payment, a fee demand or a personal account transfer, speed matters more than completeness. In India, call the national cyber fraud helpline 1930 as soon as you realise what has happened, then file the detailed complaint with your evidence on the government portal at cybercrime.gov.in. Reporting quickly improves the chance that funds are still traceable; waiting for one more support reply usually does not.
Our walkthrough on how to report online gaming fraud sets out what each channel asks for and the order to approach them in. File once, properly documented, rather than several times in fragments.
Red Flags and When to Stop Chasing the Balance
Some signals are strong enough, on their own, to end the relationship rather than prompt another attempt. The clearest is directional: deposits work flawlessly every time while every payout fails for rotating, vague reasons. A payment setup that can reliably pull money in can reliably push it out. When only one direction ever functions, the problem is intent, not infrastructure.
Minimums or limits that rise exactly when you try to cash out
Documents demanded repeatedly, or demanded through chat apps rather than in-app
Any payment tied to the release of an existing balance
Support that only works through a personal number or a single named agent
Account closed or chats cleared shortly after you raise a complaint
Pressure to recruit others as a condition of being paid
None of that makes any specific named app anything in particular – these are patterns to weigh, and the judgement is yours. But the practical maths is unkind. Each additional deposit made to recover a blocked amount increases the loss with no mechanism that would reduce it, because nothing about depositing changes whether a platform intends to pay.
Draw the line in advance and in writing: no release payments, no new deposits after a hold, no recruiting. Then shift your effort from recovery to documentation and reporting, which is where the remaining leverage actually is.
If a stuck balance has you depositing money you cannot afford to lose, or losing sleep over it, that is worth treating as seriously as the money. Free, confidential support exists: in India, the Tele-MANAS helpline on 14416 operates around the clock in multiple languages. Reaching out early is a practical step, not an admission of anything.
Frequently Asked Questions
Why is my withdrawal pending for days?
Usually for an administrative reason: verification still under review, a name mismatch between your profile and bank account, unmet bonus turnover, a first-payout check, an amount outside the limits, or fixed batch processing times. Work through those in order. A hold that clears inside the stated window is routine; one with a new explanation every day is not.
Why does an app ask for another deposit to unlock a withdrawal?
Because the demand works, not because payments require it. No bank or UPI channel needs the recipient to send money before receiving money, so a deposit tied to releasing an existing balance is a pressure tactic. It typically starts small, then escalates into larger fees. Stop depositing, document the demand and report it.
Should I pay a fee or tax to release my winnings?
No. Genuine deductions come out of the amount being paid; they are never collected from you in advance through a separate channel. Processing fees, activation deposits and tax clearance payments demanded to free a balance almost always produce a fresh demand rather than a payout. Treat the first such request as the stopping point.
What evidence should I collect when a withdrawal is blocked?
Screenshot the request with amount, date, time and status, plus the full transaction history. Save every support chat, agent name and payment demand, any UTR shown, the app version and website address, and your own bank statement entries. Export it all to your own device, because accounts and chat logs can disappear without notice.
If an app has taken your money and gone quiet, the fastest way to report online gaming fraud in India is a phone call, not a forum post. This walkthrough covers the golden hour, the 1930 helpline, filing on the national cybercrime portal, the evidence to collect before you start, and what realistically happens afterwards. It is awareness information for adults aged 18 and above.
Table of Contents
Why Gaming Payment Fraud Needs Its Own Route
Most advice about recovering money after online fraud is written for a different kind of crime. Card skimming, OTP theft and SIM-swap cases involve money leaving an account without the owner’s knowledge. Gaming-payment fraud is the opposite: you authorised every transfer yourself, usually in instalments, often to a different destination each time. That difference changes what you need to collect and how you describe it.
It also changes the shape of the loss. A single unauthorised debit is one transaction with one timestamp. A frozen payout or a vanished app is typically a chain of small deposits spread over days or weeks, tangled up with chat messages, referral links and a balance shown on a screen you never controlled. Specifics are what move a complaint, so the chain has to be reconstructed first.
Every transfer was authorised by you, so no bank alert flagged it in advance.
Payments often went to several UPI IDs, QR codes or agent accounts rather than one merchant.
The website, app name or group chat may already have changed or disappeared.
The balance you were shown was a number inside the operator’s own system, not money held for you.
Deposits sit mixed in with ordinary spending in your statement, so each one needs identifying.
If you are reading this before anything has gone wrong, the recruitment and pressure patterns are worth knowing in advance. Our breakdown of cricket ID scam warning signs covers the approaches that almost always come before a payment problem.
The Golden Hour: Why the First Minutes Decide So Much
In cyber fraud reporting, the “golden hour” describes the short window immediately after money leaves your account, while a report still has a realistic chance of catching the funds before they move on or are withdrawn. Public advisories describe it slightly differently — some say the first hour, others the first one to two hours after the debit — so treat any specific figure as illustrative rather than a hard deadline.
The mechanism behind the urgency is straightforward. When a financial cyber fraud is reported, the complaint is passed to the bank or payment provider that received the money so the suspected amount can be placed on hold while it is examined. That only works while the money is still somewhere in the system. Once it has been moved through several accounts or cashed out, there is nothing left to hold.
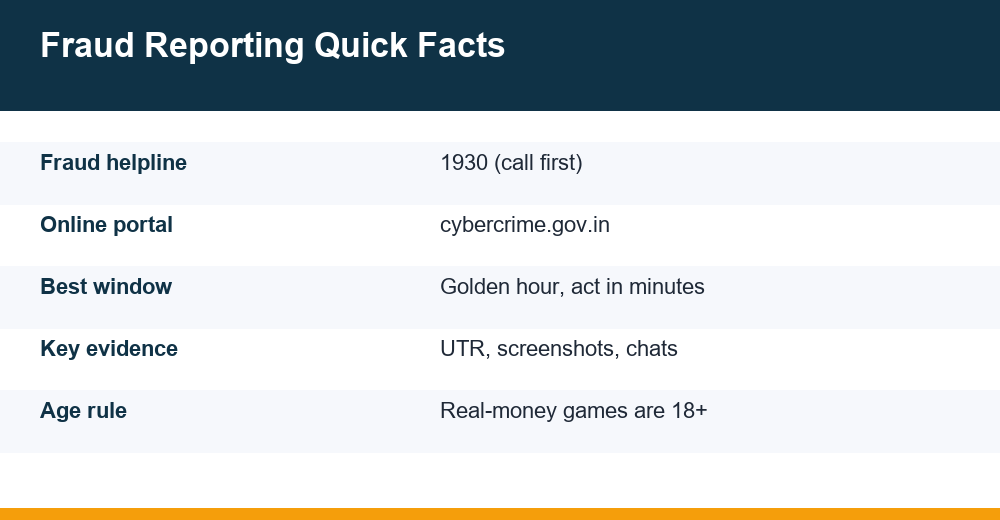
Speed beats completeness. A rough report made in twenty minutes is worth more than a polished one filed next week, which is why people who report online gaming fraud immediately tend to fare better than those who spend days assembling paperwork. Call first with whatever you have, then add the detail in your written complaint.
Stop every further payment. Decline pending collect requests and pay no “release”, “tax” or “unlock” charge.
Note the last transaction: amount, time, and the UPI ID or account it went to.
Call 1930 and report the loss, even with only partial details to hand.
Screenshot the app, the wallet balance and the payout request before anything is deleted.
Contact your bank or payment app so the transfers are flagged on their side as well.
Evidence First: The Details You Need Ready
The question people ask most is what details you need to report online gaming fraud properly. The short answer: anything that ties a rupee amount to a timestamp and a destination. A complaint saying an app cheated you goes nowhere; dated transactions with reference numbers give someone a trail to follow.
Build the file before links start dying. Operators rotate domains, rename apps and delete group chats quickly, and a screenshot you did not take is usually impossible to recover later.
Evidence
Where to find it
Why it matters
UTR of every transfer
UPI app history or bank statement
Uniquely identifies each payment for tracing
Destination UPI IDs or accounts
Payment confirmation screens
Shows where the money actually went
Withdrawal request screenshots
In-app wallet or payout history
Records that you asked and were refused
Chat logs with agents
Exported WhatsApp or Telegram threads
Captures demands and promises with timestamps
App name, version and web address
Browser address bar or app info screen
Platforms switch domains to shed complaints
Dated summary of amounts
Your own note or a simple spreadsheet
Lets you report quickly and consistently
Export chats rather than screenshotting them, because exports preserve timestamps and sender details. Keep payment receipts unedited too; cropped or annotated images carry less weight as supporting material than the originals do.
One check is worth doing first: confirm the problem really is fraud and not a stuck transfer. Money that left your bank but never reached the app has its own set of fixes, covered in our explainer on a deposit not credited to a gaming wallet.
How to Report Online Gaming Fraud Step by Step
There are three channels, and they are not alternatives. Use all three, in this order, because each one does something the others cannot.
Call the 1930 helpline and report the financial loss straight away.
File the written complaint on the national cybercrime portal with your evidence attached.
Notify your bank or UPI provider separately so the destination accounts are flagged on their side.
What is the 1930 cyber fraud helpline?
1930 is India’s dedicated helpline for reporting financial cyber fraud, run under the Indian Cyber Crime Coordination Centre. The call is where the clock starts: your report is registered and a hold request can be sent onward to the bank or payment service that received the money. Keep the last transaction details and your own account number in front of you before dialling.
Nobody from 1930 will ever ask for an OTP, UPI PIN or password. A caller who does is running a second fraud on top of the first. Write down the reference number you are given before the call ends, and dial only the short code itself rather than any “helpline” number forwarded to you in a chat group.
How do I file a complaint on the cybercrime portal?
The written complaint goes to cybercrime.gov.in, the Government of India’s portal for reporting cybercrime online. Reporting a financial fraud means registering with a mobile number and verifying it by OTP, then entering the incident details, the transaction information and your uploaded evidence. Complaints are handled by the authorities in the state you select, and you receive an acknowledgement number for tracking.
Choose the route for reporting other cybercrimes and register with your mobile number.
Enter the incident details: dates, amounts, platform name and how you were first approached.
Add each transaction individually with its UTR, amount, date and destination identifier.
Upload the evidence file — screenshots, statements and exported chat logs.
Save the acknowledgement number and a copy of the submitted complaint.
The portal publishes its own instructions for citizens reporting financial fraud, including the information to keep ready before you start; that document sits on the national cybercrime portal. Filing costs nothing, and the acknowledgement number lets you check progress later.
Should You Also Inform Your Bank or UPI App?
Yes, and as a separate action rather than an afterthought. The helpline and the portal work through one channel; your bank and payment app work through another. Telling them that the accounts you paid are linked to a suspected fraud lets them flag the transfers on their side and explain what their own dispute process allows in your case.
Use the bank’s official number from your passbook, card or app — never a number sent to you in a group or by an “agent”. Fake recovery agents are a known follow-up scam aimed squarely at people who have just lost money and are searching for help.
Report through the registered helpline, your branch, or the official in-app complaint form.
Give the date, amount and UTR of every disputed transfer, not just the largest one.
Ask for a written complaint reference rather than a verbal assurance.
Mention that you have already reported to 1930 and filed on the cybercrime portal.
Refuse any offer to recover funds in exchange for an advance fee.
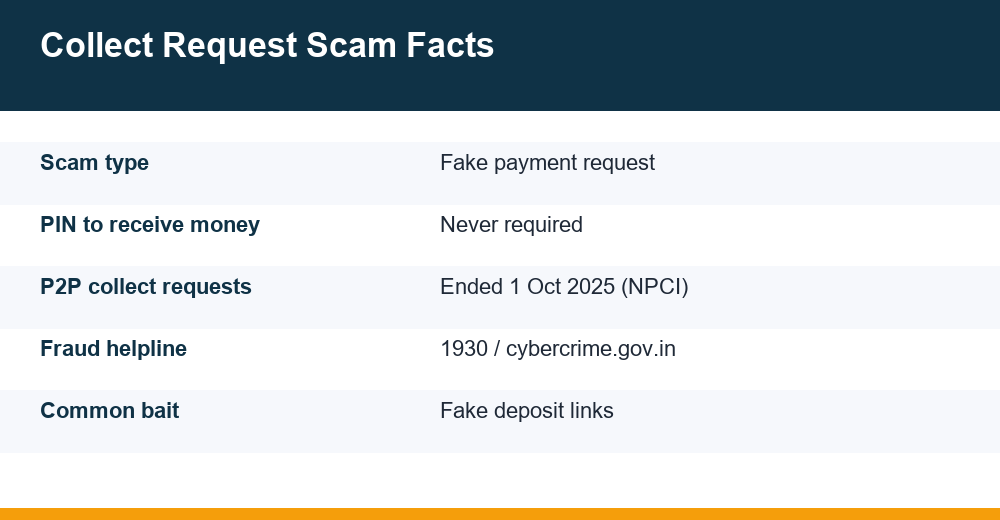
If the money left after you approved a payment request that appeared on your phone, rather than a transfer you started yourself, read our note on the UPI collect request scam first. Being able to describe exactly what you approved, and when, makes the conversation with your bank far shorter.
After You File: Tracking and Realistic Expectations
Once you report online gaming fraud, the acknowledgement number becomes your handle on the case. Keep it alongside the evidence file, and store both somewhere other than the phone the app was installed on, in case that device has to be reset.
Can you get your money back after reporting a fraud?
Sometimes, partly, and realistically only when the funds were caught before being moved on. Reporting is what makes a hold possible; it does not make one certain. The outcome depends on how fast the report went in, whether the receiving account still held anything, and what the examination that follows concludes. Treat recovery as a possibility, never as a plan.
Expect follow-up contact rather than instant resolution, and expect to supply the same transaction details more than once. Keep every communication and reply promptly when clarification is requested, because unanswered queries are where complaints go quiet.
There is a second reason to file even when recovery looks unlikely. Reports are how repeated destination accounts, recycled domains and agent networks get mapped. A complaint that does nothing for your own loss can still shorten the life of the operation that caused it.
Common Mistakes That Weaken a Complaint
Most complaints that stall do so for predictable reasons. Running through this list before you file is usually quicker than fixing the gaps afterwards.
Paying an “unlock”, “tax” or “verification” charge in the hope of releasing a balance.
Waiting days to gather perfect paperwork before making the first call.
Uninstalling the app or leaving the group chat before exporting the evidence.
Reporting one transaction when there were fifteen, leaving most of the loss unrecorded.
Trusting a “recovery expert” who makes contact after you post about the loss publicly.
Sending a stream of angry messages to support instead of one factual written complaint.
Describing the loss only in general terms, with no amounts, dates or reference numbers.
The pattern behind most of them is understandable and expensive: chasing the balance instead of closing the tap. Money sent after you realise something is wrong rescues nothing; it is simply a second loss stacked on the first, and it is money the reporting process cannot help you with either.
Closing the Tap and Looking After Yourself
With the evidence saved and the reports filed, remove the pressure channels. Leave the groups, block the agents, and uninstall the app after — not before — you have your screenshots. Cancel any autopay mandate or standing payment permission you set up for deposits, then read through your statement for recurring debits you no longer recognise.
Change the password on any account that shared credentials with the platform, particularly if you reused a banking or email password. Treat any “refund” or “compensation” message arriving in the following weeks as a fresh approach rather than good news; lists of people who have already lost money are traded and reused.
It is worth saying the plain part plainly. These are chance-based games with a built-in house edge, real money is genuinely at risk every round, and they are for adults aged 18 and over only. No reporting process changes those odds, and nothing sold in a chat group beats them either.
If the loss has left you anxious, in debt, or unable to stop thinking about winning it back, support exists. Tele-MANAS, the government’s free mental health helpline, can be reached on 14416 and operates around the clock in multiple languages. Talking it through with someone is a stronger next step than another deposit, every single time.
Frequently Asked Questions
What is the golden hour in cyber fraud reporting?
The golden hour is the short period right after money leaves your account, when a report can still reach the receiving bank before the funds are moved on. Advisories describe it as roughly the first hour or two after the debit, so treat the timing as illustrative. Practically, report within minutes rather than waiting to gather complete paperwork.
What details do I need to report online gaming fraud?
Have the UTR of every transfer, the destination UPI IDs or account numbers, dated screenshots of your wallet and withdrawal requests, the platform’s exact app name and web address, and exported chat logs with any agent. Add a simple dated summary of amounts. Unedited originals with visible timestamps carry considerably more weight than cropped images.
Can I get my money back after reporting a fraud?
Sometimes, and only partly. Reporting quickly makes it possible for the receiving bank to place suspected funds on hold, but nothing is guaranteed once money has been moved through several accounts or withdrawn. Outcomes depend on timing and what the examination finds, so treat recovery as a possibility rather than an expectation.
Should I also inform my bank or UPI app?
Yes, as a separate step from the helpline and the portal. Your bank can flag the disputed transfers and tell you what its own dispute process covers. Always use the official number printed on your passbook, card or app, never one shared in a chat group, and refuse anyone offering recovery for an advance fee.
The KYC documents gaming apps ask for – Aadhaar, PAN, bank proofs, selfies – are the same documents a fraudster needs to open loans and mule accounts in your name. Most search results on this topic come from verification-software vendors rather than from anyone trying to protect the person uploading the file. This breakdown covers which requests fit a normal pattern, which ones should stop you cold, and what to do if your documents are already out there.
Table of Contents
Why Gaming Apps Ask for Aadhaar or PAN
KYC stands for Know Your Customer – the identity check a business runs before it lets you move money in or out. On a real-money platform the stated purpose is usually threefold: confirming you are a real, single person rather than one of twenty duplicate accounts, confirming you are an adult, since real-money play is 18+ only, and matching the bank account you withdraw to with the identity you registered under.
The KYC documents gaming apps collect fall into two baskets. Identity proof – normally Aadhaar or PAN – establishes who you are and your age. Payment proof – a bank statement header, a cancelled cheque, or a UPI handle confirmation – establishes that payouts land in an account carrying your own name, which is a basic anti-fraud control rather than a formality.
It is worth knowing what each document gives away. An Aadhaar copy carries your name, photograph, date of birth and often your address in one file. A PAN copy ties you to a permanent financial identity you can never rotate the way you rotate a password. A bank proof adds an account number and, with a careless crop, a transaction history nobody asked for. Sensitivity is not equal across the three, so neither should your caution be.
That is the theory. The problem is that an identical-sounding request can come from two very different senders: a structured app with a published privacy policy and an in-app upload field, or an anonymous operator on WhatsApp who stores your Aadhaar in a phone gallery and a few forwarded chats. The document is the same; the exposure is not remotely the same.
One thing deserves stating plainly before any document enters the picture. Every game of chance on these platforms carries a built-in house edge, outcomes cannot be predicted or steered, and money you deposit is genuinely at risk. Verifying your identity does nothing to improve those odds – it only widens the circle of people who know exactly who you are.
KYC Documents Gaming Apps Request: Normal vs Risky
Not every request deserves the same answer. The KYC documents gaming apps genuinely need are a narrow set: one identity proof and one payment proof, uploaded inside the app itself, at a predictable moment – usually before your first withdrawal. Anything outside that pattern should slow you down rather than hurry you up.
Request
Typical context
Risk signal
Masked Aadhaar or PAN via in-app upload
Before first withdrawal
Normal if the app has a privacy policy and a support channel
Selfie or liveness check inside the app
Age and identity match
Common; confirm it never leaves the app
Bank proof for the withdrawal account
Matching payout account to your name
Normal; share only the page showing name and account
Full Aadhaar photo sent on WhatsApp or Telegram
Chat-based ‘ID agent’
Dangerous – no custody, no accountability, no deletion
Aadhaar OTP read out to an ‘agent’
Caller offers to ‘complete KYC for you’
Never legitimate; an OTP authorises actions in your name
Documents demanded before any deposit or play
Account barely created
Suspicious – a harvesting pattern, not a verification one
Passport, voter ID and PAN together
‘Verification failed, send more’
Escalating demands are a classic data-collection tactic
Timing is the most reliable tell. Genuine checks cluster around withdrawal, because that is the point where money leaves the platform and identity actually matters. Harvesting requests cluster at signup, arrive over chat apps, and escalate step by step: first PAN, then Aadhaar, then a selfie holding the card. No ordinary verification process needs a photograph of you holding your Aadhaar up to your face for a gaming account.
The second tell is the channel. An upload field inside an app creates a record and a responsible party you can write to. A WhatsApp chat creates neither – the file simply sits in someone’s phone, forwardable in a single tap, with no deletion you will ever be able to verify.
One question settles most cases: what is the smallest version of this document that answers the request – masked instead of full, cropped instead of complete?
Is It Safe to Upload Your PAN Card?
It depends entirely on where the upload lands, so the honest answer is: sometimes, and only with precautions. PAN is a permanent identifier. Unlike a password, you cannot reissue it after a leak and walk away clean. Indian reporting has repeatedly described fraud groups using harvested PAN and Aadhaar copies to apply for instant loans in other people’s names, with victims finding out from a recovery call.
Before any PAN upload, apply the same diligence you would apply to the platform itself. Our verification checklist to run before any deposit covers the platform-level questions; for the document itself, work through these:
Upload only inside the app or its official website – never over chat, email, or a link somebody sent you.
Add a visible purpose watermark across the image: the platform name and the date, written diagonally over the card rather than tucked in a corner, so the copy is useless anywhere else.
Crop or cover anything the request does not need. A PAN check never needs your bank balance, your salary line, or your family details.
Keep your own record: screenshot the upload screen with the date, so you can later say precisely what you shared and with whom.
Check your credit report periodically for loan enquiries you never made – that is usually how PAN misuse surfaces first.
Never send a document twice because ‘the first one did not go through’. Re-requests are a standard pressure script.
If a platform cannot say in writing why it needs PAN, where the file is stored, and how you can have it deleted, that silence is itself the answer. An operator casual about your identity before you deposit will not become careful about your money afterwards.
Masked Aadhaar and Virtual ID, Explained
UIDAI offers two tools that let you prove identity without handing over your full Aadhaar number, and almost nobody collecting your documents will volunteer that they exist. Knowing both changes the balance of the conversation.
Masked Aadhaar
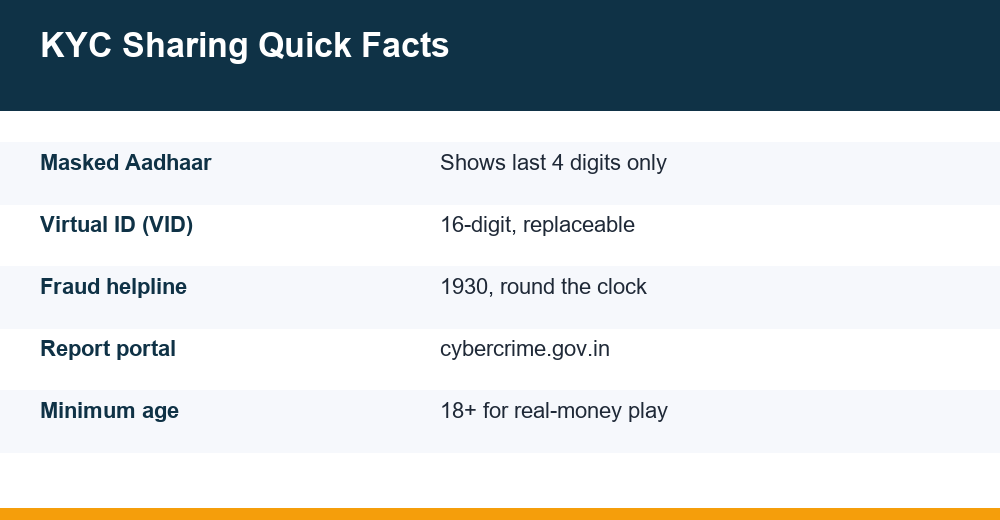
A masked Aadhaar is an official download of your Aadhaar in which only the last four digits of the number are visible; the earlier digits are hidden. It still carries your name, photograph and demographic details, so it works perfectly well as identity and age proof. Crucially, it is issued by UIDAI itself – this is not a do-it-yourself edit with a black rectangle, which a verification team is entitled to reject.
Open the UIDAI website or the mAadhaar app and choose the Aadhaar download option.
Select the masked version where the download screen offers it.
Authenticate with the one-time password sent to your registered mobile number.
Save the password-protected PDF, and open it to confirm the digits are genuinely hidden before you send it anywhere.
Menu labels change from time to time, so treat the sequence above as the shape of the process and follow whatever the current screen says.
Virtual ID (VID)
A Virtual ID is a temporary 16-digit number mapped to your Aadhaar. Where a service performs Aadhaar-based authentication, you can supply the VID instead of the real number. The Aadhaar number cannot be worked backwards out of a VID, and you can generate a fresh one whenever you like, which effectively retires the old one. Generate it through the UIDAI site or the mAadhaar app, use it, then replace it.
The practical rule is easy to remember. When a platform wants Aadhaar as a document image, send the masked version. When a flow wants the Aadhaar number for authentication, give a VID and replace it afterwards. If a requester refuses a masked copy and insists on all twelve digits for an ordinary gaming account, treat that refusal as a red flag rather than a technicality – age and identity confirmation simply does not require the full number.
What Fraudsters Can Do With Leaked KYC
Understanding the downstream damage explains why the KYC documents gaming apps and chat-based agents collect are such a prized target. A clean Aadhaar-plus-PAN pair with a selfie attached is close to a complete identity kit. Misuse patterns described repeatedly in Indian news reporting and police advisories include the following.
Loans taken in your name – app-based lenders with thin checks have been exploited using harvested PAN and Aadhaar copies, and the victim learns of it from collection calls or a damaged credit score.
Mule bank accounts – accounts opened on somebody else’s documents and used to move scam proceeds, which drops your name into the middle of an investigation you had no part in.
Duplicate or replacement SIM cards issued against your identity, quietly redirecting the one-time passwords that protect your bank and your email.
Impersonation elsewhere – your selfie and ID reused to clear verification on platforms you have never visited.
Bulk resale – identity sets get traded onward, so a single careless upload can resurface in unrelated frauds years later.
Two features make document leaks worse than password leaks. They are permanent: you cannot change your PAN, your date of birth or your face. And they are silent: nothing notifies you when a copy changes hands, so the first symptom is typically a loan statement for money you never borrowed.
The timeline matters too. A leaked document can sit dormant for a year before somebody monetises it, by which point the chat it came from is deleted and the account that asked for it has vanished. That gap is why prevention beats cleanup here.
This is why the familiar reassurance – ‘it is only for verification, everybody asks’ – misses the point. The question is who holds the file afterwards, and whether anyone identifiable is accountable for it.
Why a WhatsApp ID Agent Never Needs Your Documents
In the online cricket ID ecosystem, accounts are often sold through individual ‘agents’ on WhatsApp or Telegram rather than as an app-store product. Whatever you make of that model, one rule holds without exception: a person handing out login credentials over chat has no verification role whatsoever. He operates no identity system, keeps no audit trail, and answers to nobody you can reach. A government document sent to him serves one function – his possession of it.
The extraction scripts are predictable once you have seen them. ‘Aadhaar needed to activate your ID.’ ‘PAN required or your withdrawal stays blocked.’ ‘Send a selfie holding your card for higher limits.’ Each one borrows the vocabulary of verification while having none of its substance. The blocked-withdrawal version works best, because by then your money is hostage and the document starts to feel like the ransom.
Several of these scripts overlap with the broader patterns in our cricket ID scam warning signs breakdown: manufactured urgency, goalposts that keep moving, and fresh demands for money or data that appear only once you are invested. Document requests over chat belong on exactly that list.
If you deal with any provider despite the risks, the minimum standard is the one set out in our provider vetting checklist: a structured platform, written policies, in-app flows – and zero government documents over chat, ever. No account and no blocked balance is worth a permanent identity leak, because the balance is recoverable in principle and the identity is not.
Telling a Genuine KYC Request From a Harvesting Attempt
No single marker separates real checks from harvesting. What works is a cluster: genuine requests tend to pass all six tests below at once, while harvesting attempts fail two or three of them straight away.
Channel test: the upload happens inside the app or on the official site – never over WhatsApp, Telegram, email, or a link pasted into a chat window.
Timing test: the request appears at a logical moment, typically before a withdrawal, rather than seconds after signup or midway through a conversation with a stranger.
Scope test: one identity proof and one payment proof. Demands for several IDs together, or a selfie holding your card, exceed anything a gaming account needs.
Alternative test: a genuine process accepts masked Aadhaar or a Virtual ID. A harvester insists on the full, unmasked document and gets irritated when you ask why.
Pressure test: real verification waits. Countdown timers, ‘last chance’ messaging and threats of a frozen balance are persuasion tactics, not procedure.
Accountability test: there is a named entity, a published privacy policy, and a support channel that will answer plain questions about storage and deletion.
Apply the tests before uploading, not afterwards. The asymmetry is brutal: saying no costs you one account on one platform, while saying yes to the wrong requester can cost months of paperwork and a credit record you have to argue about. When in doubt, the KYC documents gaming apps genuinely require can wait a day while you look up the operator’s footprint, history and policies.
Keep the whole decision in proportion as well. This is an entertainment expense category where losses are the statistically expected outcome over time, because the house edge is built into the maths rather than bolted on. If protecting a deposit is what is pushing you to override your own instincts about a document, the signal is about the deposit, not the document.
Already Shared Your Documents? Response Checklist
If you have already sent Aadhaar, PAN or a selfie to somebody you now distrust, assume the file will be misused and get ahead of it. Speed matters most wherever money is involved, so take the steps in order.
Money already gone? Call the national cyber fraud helpline 1930 straight away – it runs round the clock, and fast reporting improves the chance that fraudulent transfers can still be frozen.
File a written complaint on the National Cyber Crime Reporting Portal, the government’s official channel for cybercrime, which also accepts identity-theft reports where no money was lost. Save the acknowledgement number so you can track the case.
Lock your Aadhaar biometrics through the UIDAI website or the mAadhaar app, and generate a fresh Virtual ID so any number somebody noted down stops working for authentication.
Review your Aadhaar authentication history on the UIDAI portal for verifications you did not perform, and raise anything unfamiliar with UIDAI directly.
Pull your credit report and read it line by line for loan accounts or enquiries you never made; dispute anything unfamiliar with the credit bureau in writing.
Tell your bank if the leaked set included account details or a cancelled cheque, and watch for SIM-swap symptoms – a sudden, unexplained loss of mobile signal deserves an immediate call to your telecom operator.
Preserve the evidence: chat screenshots, phone numbers, payment references, usernames and the platform name all strengthen a complaint later.
One more resource belongs here. If the situation involves money lost to gambling itself rather than fraud alone, and it is sitting heavily on you, support is available: Tele-MANAS on 14416 is the government’s free, round-the-clock mental health helpline and is meant for exactly this kind of distress. Document leaks can be contained; make sure the person dealing with them is looked after too.
Frequently Asked Questions
Why do gaming apps ask for Aadhaar or PAN?
Platforms that handle real money use these documents for three checks: confirming you are a real, single person rather than a duplicate account, confirming you are 18 or older, and matching your withdrawal bank account to your registered identity. The risk is that identical-sounding requests also arrive from anonymous chat operators who hold no verification role and simply collect documents.
Is it safe to upload my PAN card to a gaming app?
Only with precautions, and only inside an app or official website with a named operator, a published privacy policy and a working support channel – never over WhatsApp or Telegram. Write a purpose watermark diagonally across the image, crop out anything unrelated, keep your own record of what you shared, and check your credit report periodically for loan enquiries you never made.
What is masked Aadhaar and when should I use it?
Masked Aadhaar is an official UIDAI download showing only the last four digits of your Aadhaar number while keeping your name, photograph and demographic details, so it still works as identity and age proof. Download it from the UIDAI website or the mAadhaar app. Use it whenever a platform wants an Aadhaar image, and question anyone insisting on the unmasked version.
What can fraudsters do with my KYC documents?
A leaked Aadhaar and PAN pair with a selfie attached is close to a complete identity kit. Reported misuse includes loans taken out in victims’ names, mule bank accounts opened to move scam money, duplicate SIM cards that intercept banking passwords, and onward resale to other fraud networks. Unlike a password, these identifiers cannot be changed afterwards.
Telegram prediction groups promise something that sounds irresistible: advance knowledge of which colour or number lands next. This page examines the five claims those channels repeat most often, sure-shot signals, 100% accurate hacks, screenshot proof, VIP accuracy and insider access, and sets out what is actually happening behind each one. It is written for adults aged 18 and over, because every round discussed here is a chance outcome with a built-in house edge and real money at stake.
Table of Contents
Why Telegram Prediction Groups Exist
A colour-prediction round is a very short cycle: a timer counts down, players pick an outcome, the platform settles, and the next round opens within a minute or two. Telegram prediction groups sit alongside that loop, broadcasting a call before each round and claiming credit afterwards. Their existence is not mysterious once you look at the format rather than the promises.
Telegram suits this purpose for practical reasons. Channels broadcast to unlimited subscribers, admins are anonymous by default, messages can be edited or deleted without any public trace, and a channel that disappears is rebuilt within hours while the forwarded invite links keep working.
Zero accountability — an admin handle carries no verified name, address or track record anyone can audit
Instant scale — one forwarded link can add thousands of members overnight with no cost to the admin
Editable history — a losing call can be removed before most members ever open the app
No check on claims — nobody verifies an accuracy percentage before it is posted to tens of thousands of people
Who is on the other side of the keyboard?
Security researchers who have mapped colour-prediction operations describe coordinated networks promoting the same games across Facebook, YouTube and Telegram, with dedicated channels and groups used to keep followers engaged. In that structure a channel is not a neighbour sharing something useful. It is a marketing surface attached to a platform’s deposit revenue.
That distinction shapes everything below. If the channel earns when you deposit, its incentive is your continued play rather than your results, and every message it posts has to be read in that light. Our colour prediction scam how it works breakdown traces the same funnel from first contact through to the blocked withdrawal at the end.
Are These Groups Real or Staged?
The channels exist and many of the members are ordinary people. What is staged is the performance of accuracy. Most telegram prediction groups rely on one of a handful of mechanics, and once you know the shapes you can usually identify which one is running within a day of watching.
Split signals — members are divided between segments or parallel channels that receive opposite calls, so one half always sees a correct prediction and receives the congratulatory follow-up
Selective deletion — losing calls are removed, leaving a feed that reads as an unbroken winning streak
Vague framing — a message such as “big move building on the red side” can be claimed as a hit whichever way the round settles
After-the-fact posting — a call is posted or edited once the result is already known
Telegram does mark an edited message, but very few members scroll back to check, and a caption attached to an image is easy to overwrite. A channel’s own history is therefore the weakest possible evidence of its accuracy, because the admin controls what remains in it.
A test that costs you nothing
Open a notes app and record every call a channel posts, with the timestamp, before the round settles. Keep your own tally for fifty rounds without placing any money. In practice the claimed accuracy collapses towards the game’s base probability once an independent record exists, which is exactly what the arithmetic in the next section predicts.
It is also worth noting what the test does not prove. A channel that happens to score well over fifty rounds has not demonstrated a method; a coin can land heads seven times in a row. Short runs of luck are the raw material these channels are built from.
The Maths of Independent Rounds
The central claim of every signal channel is that the next outcome is knowable in advance. For a game built on independent rounds it is not, and that is arithmetic rather than opinion.
Independence means each round is generated without reference to the ones before it. A sequence of five reds does not make green due. Treating it that way is the gambler’s fallacy, and responsible-gambling educators consistently list it among the most common and most expensive misunderstandings in chance-based play.
Can anyone actually predict the next colour?
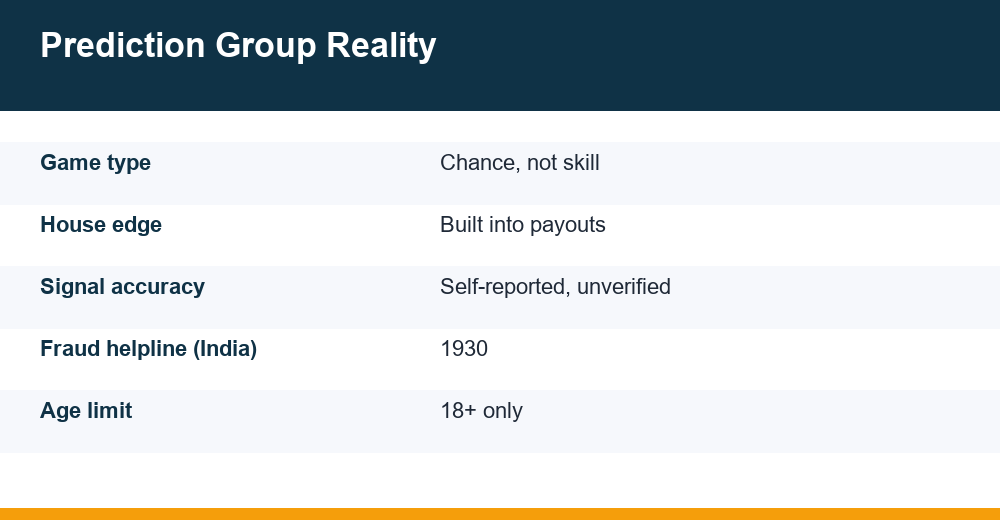
No, and the reason is structural. If rounds are independent, past results contain no information about the next one, so any system built on reading them has the same expected accuracy as a guess. If rounds are not independent, that would mean the operator influences outcomes, which is worse for a player rather than better. Either way, the advance call is not knowledge.
Then there is the house edge. Payout tables on these games are set so the platform retains a margin on everything staked. A player with genuinely average luck still trends downward over many rounds, because the payout on a win is smaller than the true odds of that win. Our colour prediction odds explained page works through those numbers with illustrative figures.
Common claim
What it implies
What is actually the case
“Sure shot signal”
The outcome is known in advance
Independent rounds carry no advance information
“100% accurate hack”
Software reads the server
A result settled server-side is not on your phone to read
“95% accuracy this week”
A verified track record
Self-reported, with losing calls deleted
“A pattern is forming”
History predicts the future
Gambler’s fallacy; history is not predictive
“VIP members rarely lose”
The paid tier performs better
Same random rounds, plus a subscription cost
How Winning Screenshots Are Faked
Screenshots are the emotional engine of telegram prediction groups, and they are also the single easiest element to manufacture. A balance figure in an image is just text.
Survivorship posting — out of thousands of members somebody won, that one image is posted, and the thousands of losses never are
Direct editing — amounts, balances and timestamps are changed in a free phone editor in seconds
Practice or demo balances — some apps display play-money totals that look identical to real ones
Recycled images — the same screenshot circulates across unrelated channels with the handle cropped out
Deposit-only proof — a large balance shows that money went in, not that a withdrawal ever cleared
The useful question about any win image is not whether it is genuine but whether it is representative. A channel posting five wins a day and no losses is not reporting results; it is advertising. A bank credit is the only thing that demonstrates money actually left a platform, and even a real payout to one member says nothing about the members who never got one.
Why do prediction channels post winning screenshots?
Because images bypass arithmetic. A number in a table invites scrutiny, while a photograph of a balance invites envy. Screenshots also manufacture social proof inside the group: when other members react with congratulations, newer members read that reaction as independent verification. Admins understand this clearly, which is why loss screenshots never appear in the feed.
There is a related trick in the comments. Reaction accounts that congratulate every posted win, ask no questions and never appear elsewhere are cheap to run and make a channel feel busier and more trusted than it is.
Paid VIP Channels Explained
The free channel is rarely the product. It is the funnel. After a few days of posted wins, members are invited into a paid tier described as VIP, premium or an inner circle, usually sold as a monthly fee or a share of claimed profits.
What the paid tier actually delivers is the same stream of calls about the same random rounds, now with a charge attached. Paying changes nothing about the underlying probability. The fee simply converts a free audience into direct revenue for the admin, earned whether or not a single member comes out ahead.
What is a paid VIP prediction group?
A subscription channel promising higher-accuracy calls, personal attention or bank-level signals in exchange for a fee. Inside telegram prediction groups the VIP pitch follows a predictable rhythm: free wins first, then scarcity (“only twenty seats”), then a deadline. Refunds are promised in conversation and rarely honoured, because the money usually moves person-to-person.
Fees collected by personal UPI handle or wallet transfer leave you with no merchant dispute route
Loss cover and profit-sharing promises are verbal, undocumented and unenforceable
Members who post losses or ask sceptical questions are removed, so the room always looks satisfied
A paid signal cannot outperform a random round — the price buys messages, not information
Why Groups Push Their Signup Link
Watch one of these channels for a week and a single message repeats more often than any prediction: register through this link, use this invite code, deposit through this app. That insistence is the clearest window available into how the group actually earns.
Why do prediction groups push you to register through their link?
Because referral structures on these platforms typically pay the referrer on the deposits of the people they recruit, not on whether those people win anything. Reporting on colour-prediction operations in India describes commission paid against a recruit’s deposit amount, which turns members into recruiters and rewards the volume of money going in.
Once that is visible, the channel’s behaviour becomes coherent rather than confusing. Posted wins increase deposits. VIP fees monetise belief. Referral codes attach the admin’s identifier to your account permanently. None of those revenue streams require you to withdraw successfully even once.
Ask who pays the admin — if the answer is the platform, per deposit, every call carries a built-in conflict of interest
A refusal to let you sign up directly is a commercial requirement, not a technical one
Multi-level structures reward recruiting your own friends and family, putting relationships at stake alongside money
Invite codes that cannot be removed later mean the commission relationship outlives your interest in the channel
The mechanics underneath all of this, including how a round is timed, how settlement works and when a result is actually generated, are set out in our colour prediction rounds explained walkthrough.
No Working Hack: The Breakdown
Search results and video thumbnails promise hack APKs, prediction bots, server tricks and modified app versions. There is a consistent reason none of them survive contact with scrutiny.
Is there a working colour prediction hack?
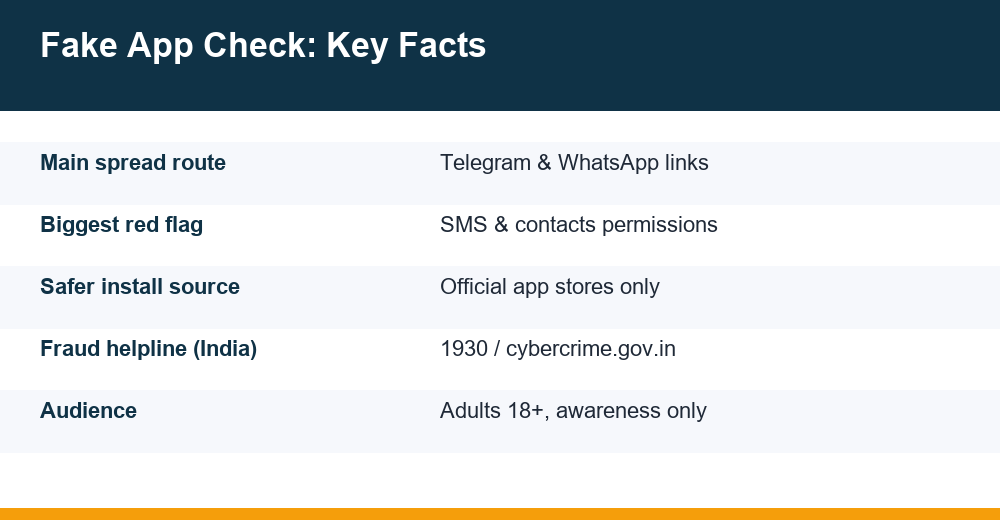
No. A result generated on the operator’s server at settlement cannot be read ahead of time by an app on your phone, because the information does not exist on your device. What the downloads do contain is the actual payload: credential-stealing code, screen-overlay or accessibility permissions, SMS access, or simply a paywall in front of a tool that outputs random guesses with a chart behind them.
Side-loaded APKs from chat links bypass app-store review completely
Tools marketed as hacks commonly request SMS and accessibility permissions, which is enough to intercept one-time passwords
A paid unlock step is often the entire business model, with the tool itself generating random output
Some versions ask you to log in with your platform credentials, which hands over the account outright
One honest qualification belongs here. Telegram prediction groups are not uniformly malicious, and plenty of members sincerely believe in the systems they share. Belief is not evidence, though, and a sincere person posting a pattern they have convinced themselves is real can cost a reader just as much as a deliberate fraud.
If a tool genuinely predicted independent random outcomes, there would be no commercial reason to sell it in a chat group for a few hundred rupees. That logic alone disposes of most of the category.
Red Flags and Protective Habits
You do not need to analyse each channel in depth. A short list of signals sorts almost all of them quickly.
Any accuracy claim above chance stated without a record anyone outside the channel can verify
Deleted or edited call history, or calls that only appear once a result is known
Fees collected by UPI or wallet transfer to a personal handle rather than a registered merchant
Insistence on one specific referral link or invite code before anything else happens
Requests to install an APK from outside an official app store
Removal or muting of anyone who posts a loss or asks an awkward question
The protective habits are equally short. Never share an OTP, PIN or password with an admin, however helpful the conversation feels. Keep your own written record of calls before rounds settle rather than trusting a channel’s summary. Treat any money sent to a channel admin as gone, because person-to-person transfers carry no dispute mechanism.
It is also worth stating the thing these channels work hardest to obscure: the outcome of each round is chance, the payout table keeps a margin for the platform, real money is at risk, and participation is for adults aged 18 and over only. No signal, subscription or download alters any part of that.
If money has already gone to a fraudulent operator, India’s cyber fraud helpline 1930 and the National Cyber Crime Reporting Portal at cybercrime.gov.in both accept complaints, and reporting quickly improves the chance of a money trail being frozen. Keep chat exports, transaction references and the channel handle.
And if the playing itself has stopped feeling optional, through chasing losses, hiding what has been spent or borrowing to continue, support exists and reaching for it early is ordinary. GambleAware’s page on the signs of gambling harms sets out what to look for, and in India the Tele-MANAS helpline on 14416 is free, confidential and available around the clock.
Frequently Asked Questions
Are Telegram colour prediction groups real?
The channels and the members are real; the accuracy is staged. Most telegram prediction groups delete losing calls, split opposite signals between segments so one half always sees a hit, or post a call once the result is known. Watching for fifty rounds while keeping your own timestamped record usually shows accuracy close to plain chance.
Can anyone actually predict the next colour?
No. In a game of independent rounds, past results carry no information about the next one, so every system built on reading history performs like a guess. Payout tables also keep a margin for the platform, which means sustained play trends downward even with average luck. Real money is at risk throughout.
What is a paid VIP prediction group?
A subscription tier sold after a run of posted wins, promising higher-accuracy calls, loss cover or personal attention for a monthly fee. It delivers the same messages about the same random rounds. Fees are usually collected by UPI to a personal handle, which leaves no merchant record and no practical route to a refund.
Is there a working colour prediction hack?
No. A result generated on the operator’s server at settlement does not exist on your phone, so no app can read it in advance. Downloads marketed as hacks typically request SMS or accessibility permissions, charge an unlock fee, or ask for your platform login. The harvesting is the product.
A deposit not credited to a colour-prediction or gaming wallet, while the money has clearly left your bank account, is one of the most common payment complaints Indian users post online. The frustrating part is that almost nobody explains where the money actually sits in the meantime. This breakdown walks through how a UPI deposit routes, what a UTR proves, when a failed debit must bounce back, and when a stuck payment is a warning sign rather than a glitch.
Table of Contents
How a UPI Deposit Actually Travels
When you tap pay on a deposit screen, the money does not jump straight from your bank into your game balance. It passes through a chain of systems, and that chain has two distinct halves: a banking leg and a platform leg. Working out where the handover broke tells you who to chase, and saves you days of arguing with the wrong desk.
The banking leg is the structured part. Your UPI app sends the instruction, your bank debits the account, the NPCI switch routes the message, and the receiving bank credits the account on the other side. This leg usually completes in seconds and leaves a permanent, traceable record that both banks can look up later.
The platform leg is everything after that. A payment gateway or the platform’s own back end has to notice the incoming payment, match it to your user ID and order number, and only then update your wallet balance. That quiet matching step is where most stuck deposits die.
Your UPI app sends the payment instruction to your bank
Your bank debits your account and passes the transaction to the NPCI switch
The beneficiary bank credits the receiving account
The payment gateway tells the platform that money arrived
The platform matches the payment to your account and credits the wallet
If the first three steps succeed, your bank’s job is finished and the debit will show as successful forever. A breakdown at step four or five is completely invisible to your bank, which is why phoning the bank first so often leads nowhere.
Deposit Not Credited: Why the Money Left Your Account Anyway
The core answer to why money was deducted but never showed up in the wallet is that the debit and the credit are two separate events. Your bank confirms the debit instantly. The wallet credit depends entirely on the platform’s systems acknowledging that payment, and several things can break in between.
Technical causes on mainstream gateways
A gateway timeout: the payment completed after the checkout window expired, so the order was already marked failed
A webhook failure: the gateway’s confirmation message never reached the platform’s server
An order mismatch: the payment arrived but could not be tied to your user ID or order number
A pending banking status: the transaction sits in limbo between banks before being confirmed or reversed
A manual review queue: unusually large or repeated deposits held back for checks before crediting
These cases usually clear on their own or after a single support ticket, because the money is sitting in a traceable corporate account and the platform has every reason to credit it rather than argue.
Causes that point somewhere darker
On anonymous colour-prediction apps, a deposit not credited can be the business model rather than a bug. Some of these apps collect money through personal UPI handles or QR codes that rotate every few hours instead of a proper merchant account. Money paid that way lands in an individual’s account, and no automated system exists to credit your wallet at all.
When the receiving side is a personal account, support can simply assert the payment never arrived, and there is no gateway record to point at. That is why the difference between a merchant-route deposit and a person-to-person transfer matters.
How Long Does a UPI Payment Take to Reflect?
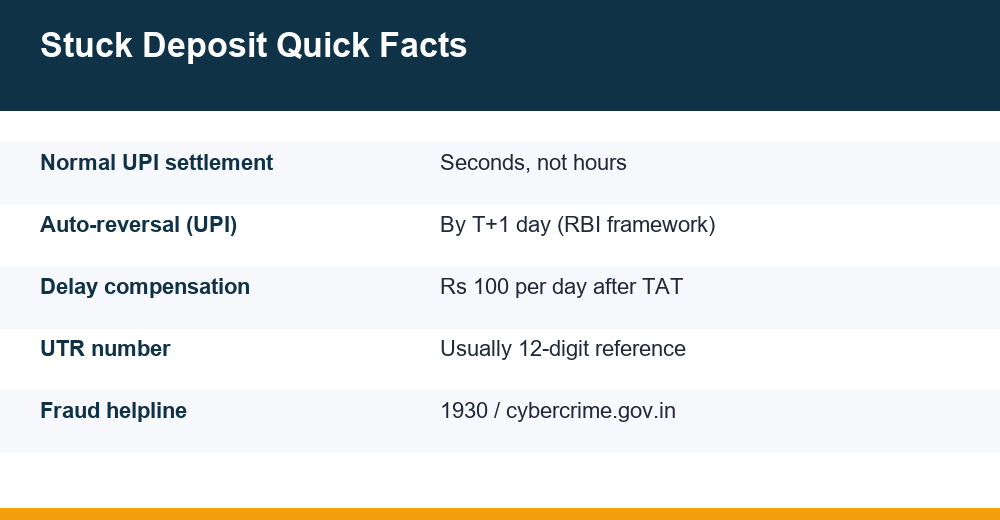
A normal UPI transaction settles in seconds. If your deposit has not appeared within a minute or two, something in the chain has stalled, but that alone does not mean the money is gone.
UPI transactions carry one of three statuses: success, failed, or pending. Pending means one bank has not yet confirmed its side. Such payments are worked out in the background and either complete or reverse, often within hours and at the outside by the next working day.
Platforms then add their own buffer on top. Many gaming and prediction apps state that deposits can take 10 to 30 minutes to reflect during busy periods. Treat such figures as illustrative; the banking leg itself is near-instant, and long platform-side delays on every deposit are themselves a quality signal.
Under 1 minute: normal, no action needed
Up to a few hours: wait if the status shows pending, and do not pay again
By end of next working day: the outer limit for automatic reversal of a failed debit
Beyond that: raise a formal complaint and start the escalation path
One practical habit matters more than all of this: never repeat a payment while the first one still shows pending. Users chasing a stuck deposit often send the same amount two or three more times, multiplying the money at risk for the sake of a balance that may well appear on its own.
It is worth remembering what the balance is for. These are chance-based products with a built-in house edge, real money is at risk on every round, and they are strictly for adults aged 18 and over. A payment delay is a reason to pause, not a reason to top up twice.
The UTR Number, Explained
The UTR, or Unique Transaction Reference, is the number generated for a UPI payment so the banking system can identify it. For UPI it is usually a 12-digit figure. It is the payment’s fingerprint: both banks, the NPCI switch and any mainstream gateway can locate the exact transaction from it. Without a UTR, a complaint is a story. With one, it is a traceable record.
Where to find it
Google Pay: open the transaction and look for the UPI transaction ID in the details
PhonePe: tap the payment in history; the reference appears in the detail view
Paytm: open the transaction detail page and check the UPI reference number
Bank statement: the reference usually appears in the narration line of the debit entry
Bank SMS alert: many banks include the reference in the debit message itself
Labels vary between apps, which trips up a lot of complaints. You may see UTR, UPI reference number, transaction reference number or bank transaction ID, and sources disagree on whether an app’s alphanumeric transaction ID is the same thing as the numeric reference. The safest move is to save every reference the app shows you, then supply whichever one the bank or support desk asks for.
A real payment team can confirm receipt against a valid reference within minutes, because that is exactly what reconciliation tools are for. A desk that keeps requesting the same reference for days, or insists it cannot trace a valid one, is telling you something about the operation it belongs to.
When Your Bank Must Reverse a Failed Transfer
Failed UPI debits do come back, and the timelines are published rather than a matter of goodwill. The Reserve Bank of India’s framework on turnaround time and customer compensation for failed transactions, in force since October 2019, sets outer limits for authorised payment systems, UPI included.
The headline scenario is exactly the stuck-deposit one: your account was debited, but the beneficiary account was not credited. In that case the transaction is to be auto-reversed, and where the reversal runs late, compensation of Rs 100 per day of delay applies. The framework also says such compensation is to be credited without waiting for you to claim it.
Scenario
Outer limit in the RBI framework
If it runs late
UPI debited, beneficiary not credited
Auto-reversal by T+1 (next day)
Rs 100 per day of delay
UPI merchant payment, no confirmation to merchant
Credit adjustment within T+5 days
Rs 100 per day beyond T+5
Transaction stuck as pending
Resolved to success or reversal in the same window
Same compensation basis
T means the transaction date, so a genuinely failed Monday deposit should bounce back by Tuesday on its own. The RBI describes these windows as the outer limit for resolution, so faster is expected and slower is the exception that triggers compensation.
Here is the catch for gaming deposits. If the banking leg succeeded, the beneficiary account was credited, and the reversal path does not apply at all. The bank delivered the money; the platform simply never passed it into your wallet. That is why checking the payment status and reference matters before you blame the bank.
A deposit not credited despite a successful banking leg is therefore a platform dispute, not a banking failure, and the pressure points change completely.
What Proof to Save When a Deposit Goes Missing
Whether this ends in a quiet wallet credit, a bank reversal or a fraud complaint, the evidence you capture in the first hour decides how strong your case is later. Chat histories get cleared by the platform, so save everything to your own device straight away.
Payment screenshot showing amount, date, time, status and the UTR or reference number
The bank SMS or statement entry showing the debit
The deposit screen or order page on the platform, including the order ID
The receiving UPI handle, account name or QR code the money went to
Every support chat, email and ticket number, with timestamps
Your wallet balance before and after the payment, if you can capture both
The receiving handle deserves special attention. If it belongs to an individual name rather than a registered business, that single screenshot can later become the centrepiece of a fraud report. Investigators can trace where money travelled far more easily when the complaint carries the exact beneficiary details.
Keep the originals rather than copies pasted into a support chat, and export them off the app if you can. If things escalate, the process for reporting online gaming fraud through official channels asks for precisely these items, and a complaint filed with a complete evidence set moves far faster than one rebuilt from memory weeks later.
One more quiet habit: log a deposit not credited incident even when the platform eventually fixes it. A pattern of repeated credit failures on the same app is itself evidence, and it should feed into whether you keep any balance sitting there at all.
What to Put in Your First Support Ticket
Most stuck deposits are resolved or refused on the strength of the first message you send. A vague complaint invites a template reply; a complete one forces a real lookup, so a deposit not credited ticket should lead with the reference number and the exact amount.
Open with one sentence stating the amount, the date and the exact time of the payment
Give the UTR or UPI reference number, then the platform’s own order ID if you have it
Name the receiving UPI handle or account the money went to
State your registered username, phone number or player ID exactly as the account shows it
Attach the payment screenshot and the bank debit message
Ask one direct question: has this reference been received, and when will the wallet be credited?
Request a ticket number and a stated resolution date in writing
Reply you receive
What it usually means
Sensible next move
Payment traced, crediting shortly
Platform-side matching failed and has now been fixed
Hold them to the stated date, keep the ticket number
No record of this reference
Either a genuine reconciliation gap or a personal-account route
Check the payment status in your UPI app, then escalate
Pay again to release the stuck amount
A demand with no legitimate basis
Stop paying and treat it as suspected fraud
Silence past the stated date
The ticket is not being worked
Move to the bank, app dispute and official channels
No reply pattern proves bad intent by itself. But a request for a second payment to free the first one is never a normal part of any payment system, and it should end the conversation rather than continue it.
Delay or Scam? Red Flags That Change the Picture
Most stuck deposits on mainstream gateways are plain delays. On anonymous prediction apps, the balance of probability shifts. No single sign proves bad intent, and no named platform deserves a verdict on one incident, but these patterns should change how you respond.
Deposits collected on personal UPI handles or QR codes that change every few hours
Support that answers instantly before payment and goes quiet afterwards
Pressure to pay again to unlock, verify or release the first stuck deposit
A deposit that credits only after you complain publicly, with no explanation offered
Deposits that always work, while cash-outs always stall
No traceable company name, address or payment partner anywhere in the app
That fifth pattern is the most telling of all. Platforms built to extract money usually credit deposits flawlessly, because deposits feed the machine, while cash-outs meet endless verification hurdles. If your money flies in but crawls out, read how withdrawals on colour-prediction apps are supposed to work, and what it means when a withdrawal gets blocked right after a large win.
Remember what these games are underneath. Outcomes are pure chance with a built-in house edge, so across enough rounds the platform keeps a margin on everything staked. A deposit that vanishes before you even play simply moves the loss earlier in the sequence.
If the evidence points to deliberate non-crediting, stop depositing and treat it as suspected payment fraud. Call the national cyber fraud helpline 1930 as soon as you can and file a complaint at cybercrime.gov.in; speed genuinely matters, because fast reporting improves the chance of money being frozen before it moves on.
The Escalation Path, Step by Step
When the waiting is over and the wallet is still empty, work through the channels in order. Each step produces a reference number that strengthens the next one, so skip nothing and write everything down as you go.
Platform support first: raise a ticket with the reference, amount, date, time and order ID, then note the ticket number and the resolution window they state
Your UPI app: open the transaction in history and use the raise concern or dispute option, which logs the case inside the official UPI dispute system
Your bank: if the transaction shows failed while the debit still stands beyond the next working day, complain to the bank and cite the RBI turnaround-time and compensation framework
NPCI dispute redressal: if the app and the bank both stall, escalate through the NPCI’s UPI dispute redressal mechanism on its official portal
RBI ombudsman scheme: for unresolved bank-side failures, this is the final free escalation step and it costs you nothing to use
Fraud route: where the platform itself is the problem, call 1930 and file at cybercrime.gov.in with your full evidence set
Notice the fork in that path. A failed banking leg is a bank matter with published deadlines working in your favour. A successful banking leg with a deposit not credited to the wallet is a platform matter, and the pressure points are support tickets, the gateway and ultimately an official fraud complaint.
A closing word of perspective. A payment system can return a stuck deposit, but nothing returns money lost to the games themselves. These are chance-based products for adults 18 and over, and every rupee deposited is genuinely at risk. If chasing deposits has become a routine part of your week, that is the clearest signal of all to step back; free, confidential support is available through Tele-MANAS on 14416 for anyone finding it hard to stop.
Frequently Asked Questions
Why was money deducted but not credited to my game wallet?
Because the bank debit and the wallet credit are separate events. Your bank completed its leg, but the platform’s system failed to match the incoming payment to your account, usually through a gateway timeout, a missed confirmation message or an order mismatch. On apps collecting money through personal UPI handles, no automatic crediting system may exist at all.
How long does a UPI deposit take to reflect?
Normally seconds. A pending transaction can take a few hours while the banks confirm it, and a genuinely failed debit should auto-reverse by the next working day under the RBI turnaround-time framework. Platform-side crediting may add minutes in busy periods. If nothing has changed after one working day, stop waiting and start the complaint path.
What is a UTR number and where do I find it?
The UTR is the Unique Transaction Reference generated for a payment, usually 12 digits for UPI. Find it in your payment app’s transaction details, in the narration line of your bank statement, or in the bank’s debit SMS. It lets banks and gateways trace the exact payment, so quote it in every complaint with the amount, date and time.
Can my bank reverse a failed deposit?
Yes, when the banking leg actually failed. Under the RBI turnaround-time framework, a UPI debit where the beneficiary was not credited should auto-reverse by the next day, with Rs 100 per day compensation where that runs late. If the receiving account was credited, the bank’s part is done and the dispute shifts to the platform instead.
A fake colour prediction app rarely looks fake: it copies the logo, colours and round timer of a known platform, then arrives through a friendly Telegram or WhatsApp link. Cybersecurity researchers at CloudSEK found that ready-made source code for these games is openly available and even taught in online tutorials, which is why dozens of near-identical APKs circulate at any time. This page walks through six concrete checks you can run before tapping install, plus the clean-up steps if one is already on your phone.
Table of Contents
Why a Fake Colour Prediction App Is So Easy to Make
Building a fake colour prediction app does not need a development team. CloudSEK’s research into these games reported that ready-made source code is handed out on websites and walked through in video tutorials, and its analysts mapped around 60 such prediction websites promoted through hundreds of social media handles. Anyone who picks up the kit can re-skin it with a new name and logo in days.
That is why you keep meeting apps that look the same but carry different names: the interface, the countdown and even the colour wheel are often the same template underneath. The operator controls the server, the result you are shown and, crucially, the wallet. The wider trap these apps feed into is covered in our breakdown of how the colour prediction scam actually works, stage by stage.
The same research also traced APKs downloaded from those sites back to domains hosted on Chinese cloud infrastructure, with several addresses mapping to the same region. In plain terms, the app on your screen may have no connection at all to the country, company or team named in its store-style description.
One honest baseline before any checklist: even on a platform that pays out, colour prediction rounds are chance with a built-in house edge, real money is at risk, and this page is written for adults 18+ as awareness material only. No install-time check changes those odds. The checks below only help you avoid the apps built specifically to collect a deposit and disappear.
Clone kits mean dozens of lookalike apps can exist at the same time
Same template, different name and logo is the standard pattern
The operator controls both the result screen and the wallet balance
Hosting and ownership often sit far away from the branding on screen
Telegram and WhatsApp Links: The Main Delivery Route
Is it safe to download gaming apps from Telegram links? In short, no, and the reason is structural rather than a matter of luck. A file forwarded in a chat has no review process behind it. Nobody scanned it, nobody verified who uploaded it, and the same filename can be swapped for a different file an hour later. Messaging apps are delivery pipes, not app stores.
Fraud campaigns lean on chat links because they combine reach with borrowed trust: the link arrives from a group member, a self-styled mentor, or a friend who was forwarded it themselves. Channels openly advertise hack or mod builds of prediction apps, usually with a deposit attached before the file is released. That is a double warning: a tampered file plus an upfront payment.
What a Chat Link Cannot Tell You
A link in a chat can also point to a lookalike website one letter away from a real one. Before touching any download page, read the full address slowly: swapped letters, inserted hyphens or a different ending such as .net in place of .com are classic clone markers. We walk through a safer, source-by-source routine in the Daman game app download walkthrough.
Chat-forwarded APKs carry no store review and no malware scan
Hack or mod channels bundle tampered files with deposit demands
Lookalike domains differ by one letter, a hyphen or the ending
A forwarded file tells you nothing about who built or edited it
Links in chats are often rotated weekly once a domain is reported
How to Check the Package Name and Publisher
Every Android app carries a package name: a unique technical ID such as com.example.appname that stays the same across updates. A clone can copy an icon and a display name perfectly, but two apps cannot share one package name on the same phone, and a store listing’s address exposes the real one. Checking takes under a minute.
Long-press the app icon and tap App info, or open Settings, then Apps, and select the app.
On most phones the package name appears on that screen; on others, open Advanced or scroll to the bottom of the details.
If the app claims to be on an official store, open its listing in a browser: the address ends in id= followed by the genuine package name.
Compare the two strings character by character. A mismatch, or a garbled package such as com.aaa123.game, is a strong clone signal.
Reading the Publisher Like a Checklist
The publisher check follows the same logic. On an official listing, tap the developer name to see what else they publish, when the app was last updated, and whether a real website and contact address exist. A publisher with one app, created weeks ago, no site and a free webmail address deserves suspicion, however polished the screenshots look.
Developer history: several maintained apps beats one brand-new entry
Update dates: an abandoned build is a security problem on its own
Contact details: a business address and domain email, not just a chat handle
Reviews over time: a burst of five-star text posted in days reads as bought
Named company: check whether that company exists outside the listing
Permissions a Prediction App Should Never Ask For
What permissions should a prediction app never ask for? Start from what the app actually does: it shows rounds, accepts entries and displays a wallet. That needs an internet connection and very little else. Anything beyond that should stop you, especially the requests below.
SMS access can read bank alerts and one-time passwords, the keys to your money
Contacts harvests your friends’ numbers for the next wave of invites
Call logs profiles you and the verification calls your bank makes
Accessibility services let an app read the screen and tap buttons for you
Device admin rights make the app difficult to uninstall
Install unknown apps lets one bad app pull in others
On current Android versions you can review and withdraw all of this under Settings, Apps, Permissions, or through the Privacy dashboard, which shows which apps used the camera, microphone and location recently. Deny first and see whether the app still runs: a game that refuses to open without SMS access is telling you what it is really for.
Watch the timing too. Many clones ask for nothing at install, then request sensitive access at the exact moment you reach the deposit or withdrawal screen, when you are least likely to say no. A request that appears only when money is involved deserves more suspicion, not less.
Remember that round outcomes sit on the operator’s server either way. Our explainer on how prediction rounds are generated covers why no honest app needs special phone access to show you a result.
The 6-Point Checklist Before You Install
Here is the full routine for screening a fake colour prediction app, condensed into six checks. Run them in order. A single hard red flag is reason enough to walk away, because there is always another day and never a genuine reason to install something tonight.
#
Check
What to look at
Hard red flag
1
Source of the file
Where the download link lives
APK via Telegram, WhatsApp or a forwarded link
2
Website address
Spelling, hyphens, domain ending
Lookalike domain or an address that keeps changing
3
Package name
App info screen vs store listing
Mismatch or a random-looking package ID
4
Publisher
Developer page, other apps, contact details
Brand-new publisher, no site, no history
5
Permissions
Requests at install and on first run
SMS, contacts, accessibility or device admin
6
Payment setup
Where the deposit actually goes
Personal UPI handles instead of a business account
The sixth check matters even after a clean install. A genuine business collects payments through a merchant account in the company’s name, not a rotating list of personal UPI IDs or a bank account belonging to an individual. If the deposit screen shows a person’s name, treat the app as compromised regardless of how smooth the interface feels.
Notice how often urgency is doing the work: a bonus that expires in ten minutes, a group countdown, a link that will be deleted soon. Pressure to skip your own checks is itself one of the checks. Nothing genuine collapses because you waited a day and read the details properly.
How to Tell an APK File Is Fake
How can you tell if an APK file is fake before opening it? You cannot be certain from the filename, which is exactly what distributors exploit. A fake colour prediction app APK usually gives itself away through context and behaviour rather than the icon or the title.
It arrives outside any store, through a chat link or a promoted download button
The file name imitates a known brand but the version number is odd or missing
Your phone asks you to allow installs from unknown sources, a prompt that exists precisely because sideloaded files skip review
A built-in security scan flags it during install, and the page urges you to continue anyway
It demands SMS, contacts or accessibility access immediately after launch
In-app support is a personal chat number rather than any ticket or email system
The download page itself leaks signals. Pages built for these files tend to carry no company name, no address, a single call to action and text copied from other sites, sometimes with mismatched brand names left in by accident. If the page cannot say who publishes the app, the app cannot be verified.
Behavioural tells continue after launch. Fake builds often push a deposit screen before you have seen a single round, show a pre-filled bonus balance to create urgency, or loop win notifications supposedly from other users. Treat these as staging rather than features: they exist to shorten the gap between install and first payment, which is the only moment the operator needs from you.
Why Clone Apps Stay Off the Play Store
Why are clone apps not on the Play Store? Because an official store is hostile terrain for them. Listing an app means passing automated malware scanning, declaring a verified developer identity, meeting the store’s own real-money gaming rules, and leaving a permanent public record of the publisher. Each of those steps threatens an operation built on disappearing.
Distribution through chat links removes all of it. There is no review queue, no takedown notice, no rating history filling up with withdrawal complaints, and the download link can be replaced the moment a domain gets reported. Researchers tracking these campaigns describe the same game resurfacing under fresh names and new domains repeatedly, a pattern a single store listing would make obvious.
Watch out for the middle option too: a website that asks you to add a shortcut to your home screen. The icon looks like an installed app, but you are using a web page with no listing, no publisher record and no update history behind it. Convenience is the pitch; accountability is what you give up.
The honest conclusion as a user: absence from official stores is not a neutral fact about availability. It is a choice the operator made, and the burden of proof sits entirely on the app, not on you. If a platform exists only as an APK file and a chat group, you have already learned the most important thing about it.
Already Installed One? Clean-Up and Reporting Steps
What should you do if you already installed a fake app? Work in this order: cut its access, remove it, secure your money, then report. Speed matters most if money has already left your account, so do not spend time arguing with in-app support first.
Turn on flight mode, or switch off Wi-Fi and mobile data, while you work.
Before deleting anything, screenshot the app page, the deposit details, the transaction IDs and the chat or page the link came from.
Withdraw the app’s permissions under Settings, Apps, Permissions, starting with SMS and accessibility.
Uninstall it. If the uninstall button is greyed out, remove its device-admin rights first, or uninstall in Safe Mode.
Run your phone’s security scan and install any pending system security updates.
Change passwords for UPI apps, email and any account whose one-time passwords the app could have read, ideally from a different device.
Watch your bank and UPI statements closely for the next few weeks and set low transaction limits meanwhile.
If money was taken, call the national cyber fraud helpline 1930 as soon as possible and file a complaint at cybercrime.gov.in with your screenshots, transaction IDs and the download link; police advisories stress that reporting within the first minutes and hours gives the best chance of freezing funds still in transit. For broader device hygiene, India’s Cyber Swachhta Kendra publishes CERT-In’s safe internet best-practices booklet, which has a mobile section worth keeping.
Two follow-ups people forget. Tell the group or contact who sent you the link, because the same file is probably still circulating there. And if the app read your contacts, warn the people most likely to trust a message appearing to come from you.
Finally, be fair to yourself about how it happened. These operations are run by teams who do this full time, and a fake colour prediction app is built to survive a casual glance. If the losses, or the urge to win them back, are weighing on you, free support exists: Tele-MANAS, the Health Ministry’s national mental health helpline, can be reached on 14416 across India.
Frequently Asked Questions
How can I tell if an APK file is fake?
Judge the context rather than the icon. A file shared through Telegram or WhatsApp, a brand-name filename with an odd version, a prompt to allow unknown-source installs, or a security warning during install are all strong signals. After launch, immediate demands for SMS, contacts or accessibility access confirm it. When several appear together, delete the file unopened.
Is it safe to download gaming apps from Telegram links?
No. Files forwarded in chats pass no review, no malware scan and no publisher verification, and the same link can serve a different file an hour later. Fraud campaigns prefer chat distribution precisely because it leaves no public listing, no ratings and no takedown trail. Treat any app that exists only as a chat-shared APK as unverified.
What permissions should a prediction app never ask for?
A prediction game needs little more than an internet connection. Requests for SMS access, contacts, call logs, accessibility services or device-admin rights go far beyond that. SMS access is the most dangerous, because it exposes bank alerts and one-time passwords. Deny these in your phone settings, and uninstall any app that refuses to run without them.
What should I do if I already installed a fake app?
Cut the phone’s connection, screenshot the deposit and transaction details, withdraw the app’s permissions, then uninstall it, removing device-admin rights first if needed. Run a security scan and change passwords for UPI, email and banking from another device. If money was taken, call the 1930 cyber fraud helpline fast and file at cybercrime.gov.in.
The complaints we read follow a rhythm. Somebody registers on a gaming platform in the evening. Before they have finished looking around, the phone rings. The caller already knows their name and the platform they just joined, speaks with the slightly bored efficiency of someone doing a job, and explains that a verification code has been sent in error and needs to be read back so the account can be released.
By the following morning the account belongs to somebody else.
What makes this worth writing about is not that it happens. It is how reliably the timing holds. Not an hour later, not the next day. Minutes. Once you understand why it has to be minutes, the whole thing stops looking like bad luck and starts looking like what it is, which is a process with a deadline.
The deadline belongs to them, not to you
A one-time password expires. Depending on the platform it might last five minutes or ten, occasionally thirty. That window is the entire opportunity. Someone who has your number and is attempting to open or take over an account has to get the code out of you inside it, which is why the call arrives while you are still holding the phone and still half expecting a message from the service you just signed up to.
The urgency in the caller’s voice is not performance for its own sake. There is a real clock running, and it belongs to them. Everything about the script is shaped by it: the immediate reason, the pressure to act now, the refusal to let you hang up and call back. Nobody doing this has the luxury of patience.
Which gives you an unusually clean rule. Anything that cannot survive you saying “I will call you back on the number published on the website” is not legitimate. Real support can wait ten minutes. This cannot.
How they knew you had just registered
This is the part that unsettles people most, and the explanations are duller than the fear suggests. There are three common routes and none of them requires anyone to have hacked anything.
The first is that the registration never happened on the platform at all. A lookalike domain collects the number and password, and the person running it uses them immediately, because stolen credentials have a short shelf life. In this version the call is not an attack on your account. It is the account being opened, with you supplying the code.
The second is a leaked list. Numbers gathered from an unrelated breach get dialled in bulk against a platform’s login page, and the call follows an automated attempt that has already triggered a code on your handset. The caller does not know you registered. They are guessing, and the guess happens to land because you did.
The third is the least interesting and the most common: the number was passed on. Referral groups, aggregator sites and chat channels collect phone numbers in exchange for codes and offers, and those lists move around.
Where the clone problem actually begins
Of those three, the first is the one you can do something about, and the window for doing it closes before you type anything.
A copied registration page costs an afternoon to build and a few hundred rupees to host. It will look correct, because it was copied from something correct. It will have a padlock in the address bar, because certificates are free and automatic and a fake site has one within minutes of going live. The padlock tells you the connection is encrypted. It tells you nothing whatsoever about who is on the other end, and the number of people who believe otherwise is the reason the technique still works.
The only defence is boring. Type the address yourself rather than tapping a forwarded link. If the platform is BDG game register, then that string of characters, typed by hand and read back once before you press enter, is the thing you are trusting. Anything that differs by a doubled letter or a swapped pair is a different website run by different people, and it does not matter how familiar the page behind it looks.
Search advertisements deserve a specific warning here. Paid placements sit above organic results, they can be bought against a brand name by anybody, and on a phone the small “Sponsored” label is easy to miss entirely. More than one complaint we have seen began with somebody searching for a platform by name and tapping the first thing they saw.
What the code is actually worth
People hand over one-time passwords because the code feels like a formality rather than a credential. It arrives unprompted, it expires on its own, it is six digits that mean nothing. Compared with a password it feels like small change.
It is the opposite. For the few minutes it is alive, that code is worth more than the password, because it is the thing that proves possession of the handset. Support staff never need it, cannot use it, and have access to the account record without it. There is no circumstance in which a legitimate employee of any platform asks you to read one aloud. Not for a bonus, not for a refund, not to fix an error on their side.
If you take one sentence from this page, that is the sentence.
If you already gave it to them
Most people realise within a minute of hanging up. That minute is worth a great deal, because accounts in this situation are emptied quickly rather than quietly.
Change the password from a device you trust, not the one you were just talking on if there is any chance something was installed on it. Remove any saved payment method. Look for a sessions or devices screen and end everything except the one you are on, and do that before the password change rather than after, so the change does not happen while somebody else is still logged in. Then take screenshots of the account page, the transaction list and the call log.
The screenshots are the step everyone skips. A complaint raised six weeks later is settled on what you can produce, and account pages change in the meantime. A handful of images taken on the day costs nothing and is frequently the whole difference.
Where money has actually moved, your bank is the party with the power to act, and the same day matters more than the same week. Raise it with them directly, keep the reference number they give you, and do not let it sit over a weekend. We have written separately about the OTP scripts themselves, including the variants that arrive as messages rather than calls.
A note on how this reads from the inside
Written down, the whole thing looks obvious. Of course you would not read a code to a stranger. The people it happens to are not careless, though, and almost all of them could have recited that rule beforehand.
What defeats them is context. The call arrives at the exact moment a call would make sense, from someone who knows what you just did, about a thing you were already half expecting. The rule and the moment do not meet. Which is why the useful habit is not knowing the rule but deciding in advance what you will do when the phone rings, so the decision is already made by the time it does.
Strong OTP fraud protection matters more for a gaming account than almost anywhere else, because one six-digit code can hand a stranger your login, your wallet balance and your linked payment details in under a minute. Fake “support agents”, screen-sharing apps and SIM swaps are the three routes Indian players get caught by most often. This breakdown explains how each one works and sets out eight plain rules that close the door.
Table of Contents
Why Gaming Accounts Are a Soft Target
A gaming wallet is a strange mix: it holds real money, yet it usually sits behind a login far weaker than any bank’s. Plenty of cricket ID and colour-prediction accounts open with nothing more than a phone number and a one-time password. Whoever holds that code holds the account, and that includes the balance, the withdrawal settings and the linked payment details.
Fraudsters also know that players in this space already do business inside chat apps. Deposits, bonuses and “support” all happen over WhatsApp or Telegram, so a message from an unknown number claiming to be the platform’s helpdesk looks completely normal. It is the same social opening used across the wider patterns collected in our cricket ID scam warning signs checklist.
There is a third reason, and it does the real damage. Unlike a bank, most of these platforms publish no verified helpline you can ring back to check whether a caller is genuine. Victims cannot cross-check, so they comply. That verification gap is what impersonators are selling.
One honest note before the rules. These games are for adults 18+, outcomes are decided by chance with a built-in house edge, and money moved into any gaming wallet is already at risk. Good OTP fraud protection cannot change those odds. It can only stop a thief from taking what the games have not.
How Do Scammers Actually Steal OTPs?
There is no magic in OTP theft. Every method ends the same way: you, your phone or your mobile network hands the code over. Only the route varies, and each route leaves an early giveaway you can learn to spot before any money moves.
Tactic
How the code leaks
Early giveaway
Fake support call
You read the code aloud to a “verification agent”
The caller manufactures urgency, then asks for the OTP
Phishing page
You type the code into a lookalike login or deposit page
The link arrived in chat; the address is misspelt or brand new
Screen sharing
A remote-view app shows your whole screen, OTP included
“Support” insists you install an app to fix the issue
Malicious APK
A sideloaded app with SMS permission reads codes silently
A game file asks for SMS or contacts access at install
SIM swap
A duplicate SIM diverts every OTP to another handset
Your phone drops to no network for hours
Notice that none of these tactics breaks any encryption. Indian bank and police awareness material describes the same shape again and again: the fraud is a two-step attack. Personal details leak first, through a shady APK, a phishing form or an older data breach, and the OTP grab comes second, dressed up as help.
That order matters. If a caller already knows your name, your platform and roughly when you last deposited, it does not prove they are genuine. It only proves your details have travelled.
Read the message, not the messenger
Every OTP arrives with a plain description of what it authorises, and almost all carry a do-not-share warning. A code for a withdrawal says withdrawal; a code for a SIM change says SIM change. Fraudsters rely on you reading the digits and ignoring the sentence around them, because that sentence is often the only thing contradicting their story.
The OTP text names an action you did not start
The amount in the message is higher than anything you entered
The sender ID is a random number rather than a registered header
The code arrives while you are on a call with “support”
Two or three codes arrive in quick succession as someone retries
OTP Fraud Protection: 8 Rules for Gaming Accounts
These eight rules cover every theft route in the table above. None of them needs technical skill. Most are simply the discipline of pausing before a code leaves your phone.
Read the SMS before using the code. The message states what the OTP authorises, whether that is a login, a payment or a SIM change. If the text does not match what you think you are doing, stop there.
Never speak a code aloud. No genuine platform, bank or wallet asks for an OTP on a call. The request itself is the proof of fraud, and no explanation changes that.
Never install a screen-sharing or remote-support app because someone asked you to. If one is already on the phone for a legitimate work task, uninstall it the moment that task ends.
Type OTPs only into apps or pages you opened yourself, never into a link pushed to you on WhatsApp or Telegram, and never into a page reached from a search advertisement.
Refuse SMS and contacts permissions to sideloaded gaming APKs. A game has no reason to read your messages, and an app that insists is telling you what it is for.
Keep gaming logins separate. A phone number and email that are not tied to your main bank account limit how far one slip can travel.
Protect the SIM itself. Set a SIM PIN and ask your operator what extra verification it offers before a duplicate SIM can be issued on your number.
Slow down on purpose. Manufactured urgency, such as “your ID will be blocked in ten minutes”, is the one ingredient every OTP scam needs. Remove the hurry and the scam usually collapses.
Screenshot these or pin them in a family group. OTP fraud protection works best as a shared habit, because fraudsters frequently target whichever family member happens to answer the phone, not the person who opened the account.
SIM Swap: When OTPs Stop Reaching You
A SIM swap attack does not steal your codes. It steals the destination. Using leaked personal details, a fraudster persuades a telecom process to issue a duplicate SIM for your number. The moment it activates, your own SIM goes dead, and every call, SMS and OTP flows to a handset you have never seen.
The classic warning sign is a sudden, unexplained loss of network that lasts hours, sometimes preceded by strange missed calls designed to make you switch the phone off or put it on silent. Indian reporting on these cases describes victims losing large sums in the quiet window before they realise the signal is not coming back on its own.
If your phone drops to no service in an area with normal coverage and a restart does not fix it, treat it as an emergency rather than a glitch. Contact your operator from another phone immediately and ask whether a SIM change or port-out was requested on your number. Not every outage is fraud, but an outage paired with unexpected alerts almost never has an innocent explanation.
Unexplained “no service” while others on the same network are fine
A flurry of missed calls from unknown international or private numbers
SMS alerts about a SIM change or porting request you never made
Being logged out of accounts even though your passwords are correct
Transaction alerts arriving by email while your phone stays silent
Prevention here is paperwork done in advance. Ask your operator about additional verification for SIM reissue, and avoid posting your mobile number alongside your full name and city in public gaming groups. Those details are the raw material a swap request is built from.
Fake Support Agents and the Screen-Share Trap
The most damaging gaming-account takeovers start with a friendly message, not a hack. A “support executive” contacts you about a pending withdrawal, a bonus, or a login problem you happened to mention in a public group. They sound patient and professional, right up to the moment they need “one small verification”.
Why do fake support agents push AnyDesk or TeamViewer?
Remote-access tools such as AnyDesk and TeamViewer are legitimate software built for IT support, but they let another person watch your screen live. Once you install one and read out the access code, the fraudster sees every notification that lands, OTPs included, without you dictating a single digit. Indian banks have issued repeated customer advisories about this exact ploy, and the Reserve Bank of India flagged remote-access app fraud as early as 2019.
A real platform never needs to see your screen. Anything an honest support team can do, it does from its own dashboard. The install request is itself the red flag, and there is no second signal worth waiting for.
Where the fake numbers come from
Many victims are not contacted at all. They go looking for help, search for a withdrawal helpline, and call the first number they find. Bank advisories in India say plainly that support numbers found through a search engine should not be trusted; use the contact details shown inside the official app.
Unsolicited contact about a withdrawal you did not report
A request to install AnyDesk, TeamViewer or any “QuickSupport” app
Any ask for an OTP, PIN, password or card number
A promise to release a stuck payout once you “verify” with a code
Pressure to stay on the call while you complete steps
Be especially careful during account setup, when chatting with agents feels routine and nothing looks unusual. The messages involved in a typical WhatsApp cricket ID activation look very similar to the opening lines of an impersonation, which is why that flow deserves its own scrutiny.
Can Someone Get In With Just an OTP?
For many gaming platforms, unfortunately, yes. Banks usually layer a password, a device check and transaction limits around each code. A typical cricket ID or prediction-app login, by contrast, is a phone number plus an OTP, which means the code is not a second factor at all. It is the only factor. The common flows described in our Daman game login walkthrough show how little else stands between a code and a live session.
That single code can expose far more than a balance. A hijacker who gets in can typically see or change:
Your wallet balance and any pending withdrawal requests
The bank account or UPI handle payouts are sent to
Your registered phone number and recovery details
Deposit history, which reveals how much you can be pressured for
Referral contacts, meaning friends who become the next targets
This is why OTP fraud protection on a gaming account deserves the same seriousness people reserve for banking apps, even though the login screen looks far more casual. The weaker the lock, the more the key is worth.
Shared an OTP by Mistake? First-Hour Checklist
Prevention is the best OTP fraud protection, but a fast response limits the damage after a slip. Police guidance in India consistently treats the first hour after an unauthorised debit as the critical window, because money is easiest to trace or hold before it is moved onwards through other accounts. Work through these steps in order and do not stop to assign blame.
Cut the access. Log out of all sessions, change the password or PIN if the account has one, and switch off the phone’s internet if a screen-share app may still be running.
Uninstall any remote-access app the caller made you install, then restart the phone and check the installed-apps list for anything else you do not recognise.
Call your bank or UPI app and ask them to freeze the card, block the handle or flag the transaction if money has already moved.
Call 1930, the national cyber fraud helpline. It is toll-free and government-run, and the operator records the transaction reference so the receiving bank can be alerted.
File a written complaint on the National Cyber Crime Reporting Portal, attaching screenshots, SMS alerts and transaction IDs. The portal record makes every later conversation with the bank easier.
If your signal died, call your telecom operator from another phone and ask them to check for a SIM change or porting request on your number.
Who to contact
For what
Keep ready
1930 helpline
Money debited without consent
Transaction ID, amount, date
Bank or UPI app
Freezing card, handle or account
Registered number, recent debits
Telecom operator
Suspected SIM swap or port-out
Alternate phone, connection details
Platform support, in-app only
Session logout, payout detail check
Account ID, screenshots
Two cautions. Keep every message and notification, because deleting “junk” often deletes the evidence. And ignore anyone who later offers to recover your money for a fee; recovery-agent offers are a well-documented second scam aimed squarely at people who have just lost once. Reporting through 1930 and the portal costs nothing.
Everyday Habits That Keep Your Codes Safe
Most OTP theft is opportunistic. Fraudsters work through lists and give up quickly on hard targets, so a few standing habits move you off the easy list permanently.
Enable debit alerts by SMS and email so every rupee of movement pings you instantly
Review app permissions monthly and strip SMS access from anything that is not your default messaging app
Keep the phone’s operating system updated, since SMS-reading malware relies on old versions
Use an app lock on payment and gaming apps so a borrowed phone is not an open wallet
Turn off message previews on the lock screen so codes are not readable over your shoulder
Never post payment problems in public groups with your number visible, because impersonators mine those posts for fresh targets
Finally, remember what OTP fraud protection can and cannot do. It guards the account, not the odds. Chance-based games keep their house edge no matter how secure your login is, real money is genuinely at risk, and only adults 18+ should be anywhere near them. If playing itself has started to feel out of control, free and confidential help exists: the government’s Tele-MANAS mental-health helpline on 14416, and the 1930 line for money lost to fraud.
Frequently Asked Questions
Can someone access my account with just an OTP?
Often, yes. Many gaming and cricket ID logins use only a phone number plus an OTP, with no password at all, so one code means complete access. Banks usually layer PINs, device checks and limits on top, but a gaming wallet rarely does. Treat every login code with the same seriousness as a payment approval.
How do scammers steal OTPs?
Four main routes: fake support calls that talk you into reading the code aloud, phishing links that capture whatever you type, screen-sharing apps that let a fraudster watch the code arrive, and SIM swaps that divert your messages entirely. All four depend on urgency, so a deliberate ten-second pause defeats most attempts.
What is a SIM swap and how does it affect OTPs?
A SIM swap is when a fraudster obtains a duplicate SIM for your number using stolen personal details. Your own SIM goes dead, and every call and OTP is delivered to their handset instead. A sudden, unexplained loss of network signal is the classic sign, so contact your operator from another phone immediately.
What should I do if I shared an OTP by mistake?
Act within the first hour. Log out of all devices and change your credentials, ask your bank to freeze cards or UPI if money moved, call the toll-free cyber fraud helpline 1930, and file a complaint on the national cybercrime portal with screenshots and transaction IDs. Also uninstall any screen-sharing app the caller made you install.
A UPI collect request scam works by reversing the direction of a payment: you believe you are about to receive money, but the moment you approve and enter your PIN, your own account is debited. In the cricket ID and colour-prediction world, so-called deposit agents use this trick constantly, dressing a payment request up as a “deposit link” or a “credit confirmation”. This breakdown explains how the mechanic works, the five checks that expose it, and what to do in the first hour if you have already tapped approve.
Table of Contents
How the UPI Collect Request Scam Works
UPI moves money in two directions. A push payment is one you start yourself: you scan a QR code or type a UPI ID, enter the amount, and confirm with your PIN. A collect request flows the other way. Someone else asks your app to pay them, and a pending request appears on your screen, waiting for your approval.
The scam abuses that second flow. A fraudster sends you a request for, say, ₹1,999, wrapped in a story: this is your refund, your winnings, your cashback, or a step needed to “activate” an incoming credit. The notification looks official because it genuinely arrives through your real UPI app. Only the story around it is false.
If you tap approve and enter your PIN, you have authorised an outgoing payment. Nothing was hacked. No OTP was stolen. You performed a perfectly normal UPI transaction – just in the opposite direction from the one you believed. That is why the trick is so effective: it exploits haste and confusion rather than any technical flaw in the payment system.
The request arrives inside your genuine UPI app, so it feels trustworthy
A message on WhatsApp or Telegram supplies the false context around it
Round amounts, countdown pressure and “approve to receive” wording are the giveaways
The debit is instant and lands directly in the fraudster’s account
Receiving Money Never Needs a PIN
This is the single rule that defeats the whole trick, so it deserves its own section: you never need to enter your UPI PIN to receive money. Not to accept a refund, not to claim winnings, not to confirm a credit, not to “unlock” a payment. Incoming money lands in your account with zero action from you.
Your PIN exists for one purpose: authorising money to leave your account. Banks and the payment network repeat this point in every safety campaign, because fraudsters rely on people not knowing it. The moment anyone tells you to approve a request, enter a PIN or scan a code so that money can come in, the conversation has become a fraud attempt – no matter who they claim to be.
Build one habit around it. Before touching any approval screen, ask yourself a single question: am I paying, or receiving? If the answer is receiving, close the app. There is nothing for you to do. If a promised credit never arrives on its own, the promise was never real, and no amount of tapping would have made it real.
Why the confusion persists
Approval screens and payment screens look similar inside most apps, and the script is written so that you are rushing. Scammers call while the request is pending, keep you on the line, and talk you through each tap. A genuine payer never needs to supervise you while you receive money – the supervision itself is the red flag.
Language does part of the work too. Phrases such as “request accept kar lo”, “verification payment” and “refund approve karein” all describe an outgoing payment while sounding like an incoming one. Read the screen, not the sentence someone is saying to you.
The Gaming Deposit Twist: Agents and Fake Deposit Links
Generic bank warnings cover refund tricks, but the betting-ID ecosystem has its own version of the UPI collect request scam that those pages rarely describe. It targets people who already intend to pay, which makes it far harder to spot.
Here is the setup. You contact an “agent” on WhatsApp or Telegram to top up a cricket ID or a colour-prediction wallet. Instead of giving you a UPI ID to pay, the agent says they will send a deposit link or a “payment request for faster credit”. What arrives is a collect request – sometimes for the amount you agreed, sometimes inflated, sometimes sent twice in the hope you approve both.
Because you were planning to pay anyway, approving feels natural. But you have now paid a personal account with no record of what it was for, no platform receipt and no recourse when the wallet credit never appears. The agent blames a “server issue”, asks you to pay again, and eventually blocks you. The same pattern runs through the wider con playbook in our cricket ID scam warning signs breakdown.
Notice what the agent gains from the reversal. A push payment you initiate leaves a UPI ID you can read, copy and report before any money moves. A request that lands in your app flips the tempo: you are reacting, the amount is already filled in, and the payee name is a line of text you are unlikely to read twice.
Keep the fundamentals in view as well. Even when a deposit does go through, these are chance-based games with a built-in house edge, real money is at risk, and the whole category is strictly for adults 18+. If gambling pressure or distress is part of the picture, free confidential support exists – Tele-MANAS, India’s national mental health helpline, runs 24×7 on 14416.
Can a Request Pull Money From Your Account?
A common fear is whether a stranger can simply pull money out of your account by sending a request. The honest answer is reassuring: no debit happens without your approval and your PIN. A pending collect request sitting in your app has taken nothing. Ignoring it costs you nothing. Declining it costs you nothing.
The danger lives entirely in the approval step. The scam needs your fingers – one tap on approve, then your PIN. That is also why the payment network moved against the feature itself. NPCI, which operates UPI, directed that person-to-person collect requests would no longer be processed from 1 October 2025. Before that, such requests were already capped at ₹2,000 per transaction. Verified merchant collect requests, the kind genuine businesses use, continue to work.
That change has a practical consequence today. A payment request claiming to come from an individual “agent” is not something a legitimate person can even send on the peer-to-peer route any more. If a request still lands in your app, it is arriving through a merchant route – so check whether the payee name shown is a business you actually recognise and intended to pay.
Pending requests take nothing; only approval plus PIN moves money
Person-to-person collect requests stopped being processed from 1 October 2025
Genuine merchant requests show a recognisable business name, not a random individual
When in doubt, decline – a real payee can always share a UPI ID for you to pay directly
Treat any claim that a request “must” be approved within minutes as a sales technique, not a banking rule. Nothing in the payment flow expires in a way that costs you money, and a request that lapses can always be replaced by a payment you make yourself, on your own terms, to a name you have checked.
Five Smart Checks Before You Tap Pay
Every version of this fraud collapses under thirty seconds of scrutiny. Run these five checks on any payment screen before your thumb goes near approve – above all when someone is messaging or calling you while the request sits pending.
Direction check: Does the screen say you are paying or receiving? If a PIN is being asked for, money is leaving. No exceptions.
Name check: Read the payee name the app displays, not the name in the chat window. A mismatch between the two ends the transaction.
Amount check: Does the figure match what you agreed, to the rupee? Inflated or duplicated requests are a classic move.
Pressure check: Is anyone rushing you, staying on the call, or counting down? Genuine payments survive a ten-minute delay; scams do not.
Origin check: Did you start this, or did it appear because of a link or message someone sent you? Unsolicited requests default to decline.
What you see
Genuine deposit flow
Collect scam flow
Who starts the payment
You scan or enter the UPI ID yourself
A request appears, sent by the other side
PIN usage
You enter it knowing you are paying
You are told a PIN is needed to “receive”
Payee name
Matches the business you chose
Unknown individual or lookalike name
Pace
No one hurries you
Live chat or call pressures instant approval
Record
App history plus platform receipt
Only a chat thread that can be deleted
The direction question alone catches nearly every variant, including the QR versions where scanning and entering a PIN performs a payment you believed was a credit. Say it out loud if it helps: paying, or receiving?
Variants of the Same Trick to Recognise
The collect request is one delivery method for a single idea: persuade you to authorise a payment while you think you are accepting one. Once you recognise the idea, the variants stop working on you. Each of the following has turned up in deposit and withdrawal conversations around gaming wallets.
QR code to receive: you are sent a code and told scanning it credits your wallet. Scanning plus a PIN always pays out, never in.
Screen-sharing “help”: an “agent” asks you to install a remote-view app so they can “fix” a failed deposit, then watches you type your PIN.
Overpayment reversal: someone claims they sent you extra by mistake and sends a request to “return” it. No money ever arrived.
Duplicate requests: two identical requests seconds apart, betting that you approve both while clearing notifications.
Lookalike handles: a payee name copying a known brand with one changed character, so the app display looks familiar at a glance.
Also resist the “small test payment” framing. Being asked to send or approve a token amount to “verify” an account is a way of establishing that you will comply, and the second request is rarely small. A verification that costs money is not a verification.
What Happens If You Approve a Fake Request?
The mechanics are brutally simple. The instant you confirm with your PIN, your bank treats the transfer as an authorised transaction. The amount leaves your account in seconds and reaches the fraudster, who typically moves it onward through other accounts almost immediately. There is no pending window and no built-in undo.
This is what separates the UPI collect request scam from card fraud or an account takeover. Nobody broke into anything: the system recorded you as a willing payer. Recovery therefore depends on speed – getting the trail reported before the money is layered away – rather than on proving a technical breach.
Expect the fraudster’s behaviour to follow a script after the debit. Some vanish instantly. Others stay in character, claiming the payment “failed” and sending a second request, or offering to “reverse” the first if you approve one more. That is a double-dip attempt on someone who has already shown they will tap. Any message arriving after a suspicious debit belongs to the same operation.
What approval does not do
One approved request does not hand anyone standing access to your account. It does not expose your PIN, and it does not let future requests debit you automatically. Every transaction needs fresh approval – so one mistake, caught quickly, stays one mistake rather than becoming an open tap.
First-Hour Response After a Fraudulent Approval
Money moves fast, so your response has to move faster. Fraud advisories talk about a golden hour: the sooner the trail is reported, the better the chance that banks along the chain can freeze the funds before they are withdrawn or scattered. Here is the sequence.
Call 1930, the national cyber fraud helpline. It runs round the clock and exists for financial cybercrime exactly like this.
Note the acknowledgement number you are given, then complete the complaint online on the National Cyber Crime Reporting Portal – the portal’s own instructions say registration should be completed within 24 hours.
Have the details ready: bank or wallet name, the transaction ID or UTR number, the date, the amount and the recipient’s UPI handle.
Notify your own bank or UPI app through its fraud or dispute channel, so the debit is flagged on your side as well.
Screenshot everything before it disappears: the chat, the request, the payment confirmation, and the fraudster’s number or handle.
Follow up on your complaint – and report even if hours or days have passed, because late reports still feed freezes and investigations.
Keep the evidence tidy. The portal accepts supporting documents as uploads, and a clean set – statement, transaction reference, chat thread, screenshots – is faster to act on than a scattered pile. Save copies for yourself before uploading anything.
Do not pay anyone who contacts you afterwards promising recovery for a fee; refund-recovery callers are a well-documented second wave of fraud aimed at people who have already lost money. The step-by-step evidence checklist in our report online gaming fraud walkthrough covers what investigators ask for and how to present it.
If the loss happened while topping up a betting wallet, keep that context in your report. The “agent” handle and the chat thread are precisely the details that link your case to others involving the same operator.
How to Decline, Block, and Stay Protected
Declining a collect request is always safe. Open the request in your UPI app and choose decline or reject; no PIN is needed and nothing leaves your account. Most apps also let you block or report the requester from the same screen, which stops repeat attempts from that handle and feeds the app’s own fraud signals.
A few standing habits shrink your exposure to almost nothing:
Treat every unsolicited payment request as a decline by default – a genuine payee can simply receive a payment you initiate
Never approve anything while someone is on a call or a live chat with you
Keep your UPI PIN entirely to yourself; no agent, bank staffer or “support” worker ever needs it
Review your UPI app’s settings and restrict or mute incoming payment requests where the app allows it
Use the in-app report option so fraudulent handles get flagged at the network level
Check your statement weekly, so a small unexplained debit is caught in days rather than months
Apply the same scepticism to the other direction of the pipe. Deposits and withdrawals handled through informal agents share one weakness: the safety of your money depends entirely on a stranger’s honesty, and there is no receipt to appeal to. Before sending anything, read how payout flows actually behave in our cricket ID withdrawals via UPI explainer – the red flags on the way out mirror the ones on the way in.
None of this requires technical skill. It requires one pause and one question at the approval screen, every single time. Your PIN pays; it never receives.
Frequently Asked Questions
Can someone take money from my account through a UPI collect request?
Not without your participation. A pending request takes nothing by itself – money only moves after you tap approve and enter your UPI PIN. Ignoring or declining a request costs you nothing. Since 1 October 2025, NPCI has also stopped processing person-to-person collect requests, so any request you now receive should show a recognisable merchant name.
Do I need to enter my UPI PIN to receive money?
Never. Your UPI PIN exists only to authorise money leaving your account. Incoming payments, refunds, winnings and cashbacks arrive automatically with no action from you. Anyone who says a PIN, an approval or a QR scan is needed to receive money is attempting fraud, so end the conversation and decline whatever sits on your screen.
What happens if I approve a fake collect request?
The amount debits instantly and reaches the fraudster, because your bank records it as an authorised payment made with your own PIN. That is the core of the UPI collect request scam: nothing is hacked, so recovery depends on speed. Expect follow-up messages asking you to approve again to “reverse” it – a second attempt, not help.
What should I do immediately after approving a fraudulent request?
Act within the first hour. Call the 1930 cyber fraud helpline, note the acknowledgement number, and complete your complaint on cybercrime.gov.in with the transaction ID and the recipient’s UPI handle. Alert your bank or UPI app, screenshot the chat and payment proof before they vanish, and follow up even if time has passed.